Tool sprawl in agentic AI happens when the number of tools, APIs, and integrations connected to autonomous agents grows faster than anyone can track them. Each new connection adds a credential, a permission, and a potential blind spot. The result isn’t just clutter. It’s an inventory problem that turns into a security problem, then a governance problem no single team can solve alone.
Six months ago, your sales team’s agent had access to three systems. Today it has access to nine, and nobody remembers approving the last four.
That’s not a hypothetical. It’s the default trajectory for any organization that lets agent-building outpace agent-governing.
This piece walks through what tool sprawl in agentic AI actually looks like, why agent sprawl is accelerating in 2026, and what separates organizations that keep visibility from the ones that discover their exposure during an incident review.
What is tool sprawl in agentic AI?
Tool sprawl in agentic AI is the uncontrolled growth of tool connections, APIs, and credentials tied to autonomous agents, spread across teams with no central record of what exists. It’s a close cousin of traditional SaaS sprawl, but the mechanics are different in one critical way: the thing accumulating access isn’t a human logging into a dashboard. It’s software that can act on its own.
Traditional tool sprawl meant too many licenses and duplicate subscriptions. It was wasteful, but largely passive.
Agent sprawl shares some characteristics with SaaS sprawl and shadow IT, but autonomous agents introduce a different level of operational risk because they can actively access systems and take actions. They take actions. An unmanaged agent can query a database, call an API, move money, or send a message on its own.
That distinction is why tool sprawl, agent sprawl, and Shadow AI (AI systems operating without security or IT oversight) show up together so often. They’re not the same problem, but one produces the next.
Agent sprawl describes the accumulation of agents that are difficult to inventory, assign ownership to, or retire. Shadow AI is what happens when AI tools or agents operate outside approved oversight altogether. An organization can therefore have agent sprawl without having Shadow AI, but unmanaged sprawl makes unauthorized deployments much harder to detect.
The relationship is directional. Unchecked agent sprawl produces shadow AI.
Getting ahead of that chain starts with visibility, which is the entire premise behind AI agent governance and a working AI agent registry that records what’s actually running before Shadow AI has a chance to take root.

Why is agent sprawl growing?
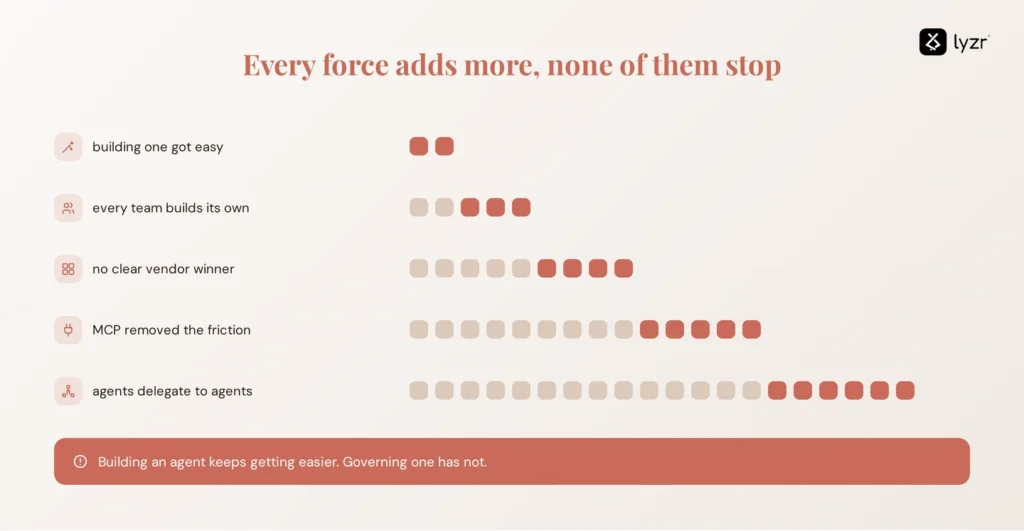
Agent sprawl is growing because building an agent has become nearly as easy as writing a prompt, while governing one hasn’t gotten any easier. Several forces are converging at once, and none of them show signs of slowing down in 2026.
The barrier to building an agent keeps dropping. Frameworks and low-code platforms let a single developer, or a non-developer with the right tool, stand up a working agent in an afternoon. Natural language interfaces are enabling more teams to build and orchestrate agents without traditional coding. The result is a rapidly expanding landscape of AI agents that no single team fully understands or controls.
Agent development is also becoming decentralized. One business unit may deploy an agent for customer operations while another builds its own workflow automation, and engineering may create separate internal agents for development or data access. Each deployment can be justified on its own. The problem appears when those systems accumulate without a shared inventory, ownership model, or review process.
Multiple frameworks and model providers compound the fragmentation. Stiff competition between vendors and fears of vendor lock-in are driving the sprawl, and enterprises are adopting multiple agents because there is no clear vendor winner in the agentic space.
Then there’s the integration layer itself. The Model Context Protocol (MCP, an open standard for connecting agents to external tools and data) made it dramatically easier to wire an agent into a new system. Before MCP, plugging an agent into a new tool required building custom schemas and writing dedicated API wrappers from scratch, and that integration friction naturally slowed deployment. Remove the friction, and connections multiply. Every new MCP server is a new tool surface, often with its own authentication and no shared logging layer, as covered in our breakdown of the agent tool registry model and our guide to what a MCP server registry actually governs.
Finally, agents don’t stop at doing their own job. They increasingly delegate. A manager agent hands work to worker agents, each inheriting or requesting its own access, a pattern that’s central to how agent orchestration works at scale, and one more multiplier on top of everything else.
What does tool and agent sprawl look like in practice?
In practice, tool and agent sprawl looks like three departments solving the same problem independently, each unaware the other two exist. Picture a mid-size enterprise six months into its agent rollout.
The sales team deploys an agent connected to Salesforce to update lead statuses. Marketing builds a separate agent wired into HubSpot and a data warehouse for lead enrichment. Engineering ships an internal agent with GitHub access and read privileges on a production database. Each decision made sense in isolation.
None of these were reviewed together. Months later, no one knows all four exist, two of them can reach customer data, one still authenticates with a former employee’s API key, and the logs are incomplete.
The compounding starts here. The marketing and sales agents begin overlapping in function, duplicating enrichment work and inflating API costs. A permissions change meant for one workflow accidentally widens what the Salesforce agent can touch. The engineering agent’s credentials, never rotated, get exposed when its code lands in a shared repository.
None of these failures is dramatic on its own. Together, they describe an organization that lost track of its own agent estate, the exact scenario a central agent registry exists to prevent. Choosing the right platform for that registry matters too, which is why it’s worth reviewing how the best AI agent registry tools compare before standardizing on one.

What are the risks of tool sprawl?
The risks of tool sprawl compound because each new connection is also a new identity, a new permission set, and a new gap in accountability. Here’s how they break down.
Risks of tool sprawl at a glance
| Risk | What happens | Governance impact |
|---|---|---|
| Identity sprawl | More agents create more non-human identities and credentials | Each identity is a potential entry point that must be tracked and secured |
| Privilege drift | Agents retain permissions from earlier tasks long after those tasks end | Access grows wider than the job the agent is actually doing |
| Data exposure | More tool connections create more paths to sensitive systems and records | Every integration is a new route to customer or financial data |
| Shadow AI | Unapproved agents operate entirely outside central visibility | Security teams cannot review or protect what they cannot see |
| Operational duplication | Multiple teams build agents that quietly perform the same task | Wasted engineering time and inflated API and infrastructure costs |
| Poor accountability | Nobody can quickly name who owns a given agent or its actions | Incident response slows down when ownership has to be traced first |
| Lifecycle gaps | Old agents, credentials, and integrations stay active long after they’re needed | Dormant access becomes the easiest target in a breach |
The scale of this is no longer theoretical. Gravitee’s 2026 State of AI Agent Security report found that AI agent fleets have roughly doubled in a matter of months, and that only 14.4% of organizations have full security approval for their entire agent fleet.
Visibility hasn’t kept pace either. The same report found that mean monitoring coverage sits at roughly 52 percent, meaning close to half of all agents in production are running without active oversight, and 88 percent of organizations reported experiencing or suspecting an agent-related security incident in the past year.
The accountability gap is arguably the hardest one to reverse after the fact. Privilege drift sets in fast. In human identity management, privilege drift occurs slowly as roles expand through job changes. With agents, it happens at development speed. By the time someone asks who approved an agent’s database access, the answer is often buried in a Slack thread that no longer exists. Centralizing how agents reach external systems through an agent gateway is one of the more direct ways to keep that sprawl from turning into a blind spot.

How can organizations control tool sprawl?
Organizations can control tool sprawl by building a continuous governance process around agent inventory, ownership, permissions, lifecycle management, and runtime monitoring.
Create a central agent registry. Record every agent’s identity, owner, purpose, tools, permissions, model, environment, and status in one place. This becomes the system of record everything else builds on.
Inventory tool connections. Know exactly which agents can reach which systems, not just which tools exist in principle. A tool nobody uses is low risk. A tool three unrelated agents all have write access to is not.
Assign ownership. Every agent needs a named business and technical owner, not a team distribution list. When something breaks, ownership determines how fast it gets fixed.
Use least-privilege access. Give agents only the permissions their current task requires, and reassess as that task changes. This is the direct countermeasure to privilege drift.
Control the lifecycle. Define explicit stages for approval, deployment, review, suspension, and retirement. Every organization has a process for offboarding people. Almost none have one for offboarding agents. What accumulates is a population of automations with valid credentials, live schedules, and no supervisor.
Monitor runtime behavior. Track what agents actually do, not just what they were configured to do. Configuration is a snapshot. Behavior is the ground truth, and it’s the foundation of effective AI agent monitoring for governance.
Reconcile the inventory regularly. Compare what’s registered against what’s actually running. This is how Shadow AI and forgotten agents surface before an incident forces the discovery. For leadership teams building this discipline top-down, the CIO playbook to AI agent governance lays out the same sequence from an executive vantage point.
Teams moving through this sequence for the first time don’t need to build it from scratch. Our playbook on taking agents to production walks through the same approval, deployment, and governance gates in the context of getting an agent live safely, which is the same discipline that keeps it governed once it’s there.
Tool registry vs agent registry vs AI control plane
A tool registry, an agent registry, and an AI control plane govern different layers of the same problem, and confusing them is how organizations end up with partial visibility instead of real control.
Registry vs control plane: layer by layer
| Layer | What it governs | Key limitation without it |
|---|---|---|
| Tool registry | Available tools, functions, and integrations agents are allowed to use | No way to know which agents actually invoke which tools in practice |
| Agent registry | Agents themselves, their metadata, ownership, and lifecycle status | Tells you an agent exists but can’t enforce what it’s allowed to do |
| AI control plane | Agent identity, permissions, evaluation, policy, runtime activity, and full lifecycle | Without it, policy exists on paper but isn’t enforced in production |
An agent tool registry is a centralized catalog for organizing, discovering, and governing the tools, functions, and capabilities available to AI agents. An agent registry generally catalogs AI agents themselves for discovery and management. Both matter, but neither one enforces anything on its own.
The registry is your system of record. A control plane is the governance and operational layer that acts on what the registry knows.
Put plainly: a registry tells you an agent exists. A control plane decides what happens next, whether that agent gets approved, what it’s permitted to touch, and whether its behavior in production still matches what it was approved for.
Once the registry becomes the system of record, organizations still need a way to act on what that inventory reveals. That’s where an AI control plane becomes useful: it connects agent identity, permissions, evaluation, runtime policy, and lifecycle controls to the registry.
Lyzr Opencontroller provides this control-plane layer, turning the registry from a passive inventory into an active governance system. It sits above the registry and turns a static inventory into an active governance system, discovering agents, evaluating them before production, and enforcing policy once they’re live.
How does an AI control plane help control agent sprawl?
An AI control plane controls agent sprawl by closing the gap between knowing an agent exists and actually governing what it’s allowed to do. That gap is where every risk in the table above lives.
Specifically, a control plane can:
- Register every agent as it’s discovered, across clouds, frameworks, and teams
- Assign each one a persistent identity, separate from the credentials it happens to be using
- Track ownership and configuration continuously, not just at creation
- Evaluate agents against safety and performance criteria before they ever reach production
- Enforce least-privilege permissions and policy in real time
- Monitor runtime activity so behavior, not just configuration, is visible
- Maintain a complete audit trail for every action an agent takes
- Flag unmanaged or unexpected agents the moment they appear
- Support the full lifecycle through to retirement and credential revocation
Lyzr Opencontroller extends that model across clouds, frameworks, and teams, giving organizations one governance layer for agents regardless of where they were built or deployed.
If your organization is somewhere between “we think we know how many agents we’re running” and “we’re certain we don’t,” it’s worth seeing what Opencontroller looks like against your own agent estate. Book a demo with Lyzr today.
Frequently asked questions
Agent sprawl is the uncontrolled proliferation of AI agents across an organization without centralized visibility, ownership, or governance. It occurs when teams deploy agents independently to automate tasks, access data, or integrate with systems, often without consistent security controls or lifecycle management. It’s the operational root cause that, left unaddressed, tends to produce Shadow AI as its downstream consequence.
Agent sprawl is the inventory and coordination problem. Shadow AI is the security consequence that follows it. Agent sprawl is the operational problem of not knowing what agents exist. Shadow AI is the security consequence of that gap. A fully sanctioned, IT-approved agent can still contribute to sprawl if it has no registered owner or lifecycle plan, even though it isn’t Shadow AI.
Shadow IT describes unsanctioned applications that store data and wait for a person to act on it. Agent sprawl describes something more active. Shadow IT meant unsanctioned applications that stored data and waited for a person. Agent sprawl means autonomous software that reads, writes, calls services, and decides without human approval.
No, they overlap but describe different failures. Shadow AI refers to AI tools and agents used without IT awareness or approval. Agent sprawl is broader. It includes fully sanctioned agents that simply lack a registry, an owner, or a lifecycle. You can have serious agent sprawl without a single unapproved tool.
Tool sprawl is caused primarily by the ease of connecting agents to new systems combined with decentralized, uncoordinated adoption across teams. Standards like MCP removed the technical friction that once slowed integrations, and Gartner has found that only 13% of organizations think they have the right AI agent governance in place, even as agent volumes climb sharply.
An agent registry is a system of record; an AI control plane is the enforcement layer built on top of it. The registry is your system of record. A control plane is the governance and operational layer that acts on what the registry knows. A registry alone can tell you an agent exists. It can’t stop that agent from taking an unauthorized action.
Book A Demo: Click Here
Join our Slack: Click Here
Link to our GitHub: Click Here