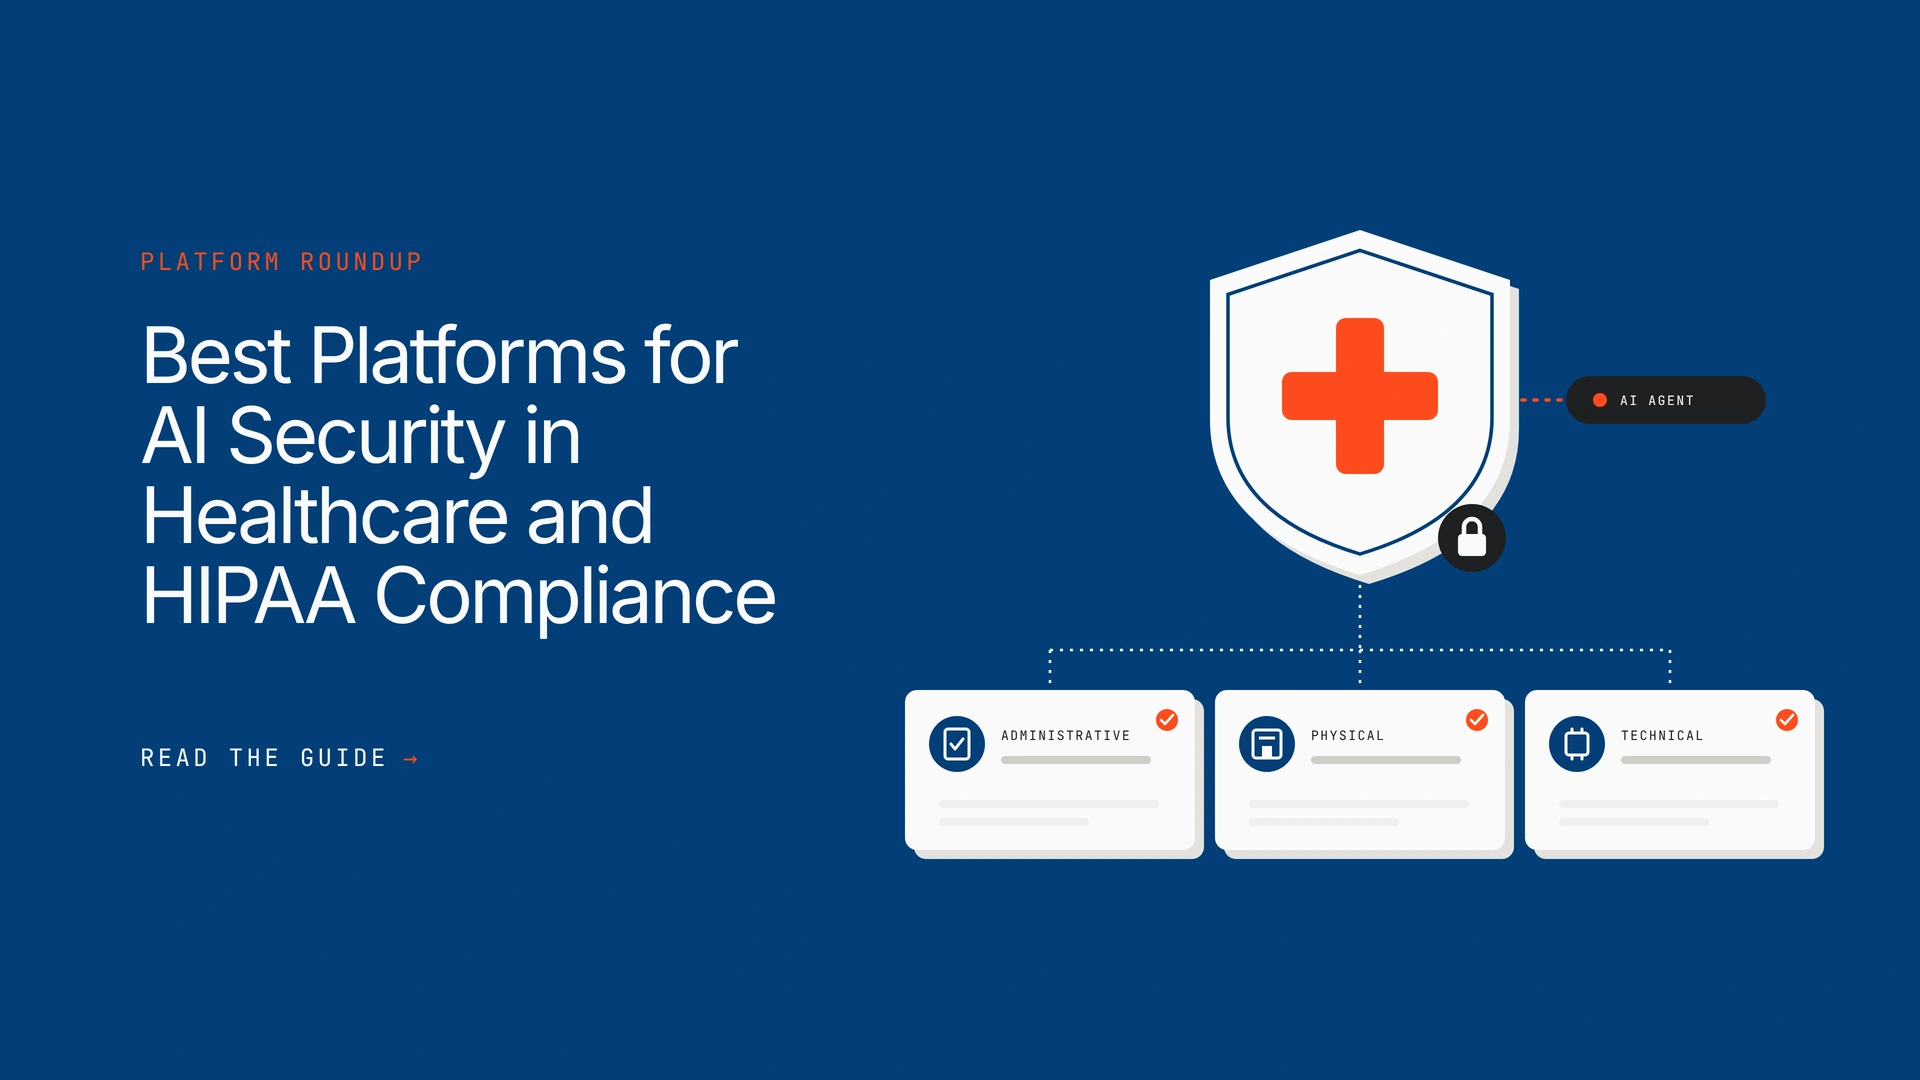
No AI platform is “HIPAA compliant” on its own: HHS does not certify products, so compliance depends on a signed Business Associate Agreement, how the platform handles protected health information, and how you deploy it. This guide compares eight options across those layers: BastionGPT and Google’s Gemini for healthcare as AI assistants, Fini, Kore.ai, Talkdesk and Hyro for patient-facing agents, Nightfall for data protection, and Iternal’s AirgapAI for local deployment. Madison, Lyzr’s agentic GRC product, is listed first as the proof layer, with a caveat that matters here: it is built for US banks and credit unions, and HIPAA is not a described Madison module. Opencontroller by Lyzr covers per-call policy and audit for agents. Read each entry’s limits before you rely on a vendor’s HIPAA claim.
TL;DR
- HIPAA is not a product feature: HHS does not certify AI tools. What counts is a signed BAA, safeguards on PHI, and a record of how you use the tool.
- Best for clinician AI assistants: BastionGPT states a BAA on its plans and no training on customer data. Google’s Gemini for healthcare, launched in preview in November 2026, adds read-only Epic and Oracle Health access but states no BAA on its page.
- Best for protecting PHI in motion: Nightfall describes PHI detection and redaction, and block and other actions across supported channels, including AI tools and MCP.
- Best for patient-facing agents: Fini, Kore.ai, Talkdesk and Hyro. Fini’s HIPAA claims are in self-published rankings, and no BAA statement appeared on the Kore.ai, Talkdesk or Hyro pages we read.
- Madison and Opencontroller: our products. Madison holds the rule-to-evidence record but is built for banks; Opencontroller governs agent calls and keeps a signed audit trail. Neither is a HIPAA certificate.
- How we judged: vendor pages and press, with gaps stated. “Not described” means we did not find it, not that it is absent.
What makes an AI platform safe to use with PHI?
An AI platform is safe to use with protected health information (PHI) when the vendor has signed a Business Associate Agreement, safeguards cover access, encryption and audit, the data is not used to train models, and your own use stays within the minimum necessary. Recent coverage describes HHS’s proposed update to the HIPAA Security Rule as still proposed: it was published on January 6, 2025, and the HIPAA Journal’s October 2026 update says the regulatory agenda now points to July 2027 or later for a final rule. Proposed requirements include mandatory encryption, multi-factor authentication and technology asset inventories, and the coverage we read describes no AI-specific provisions. Treat the proposal as direction, not law, and confirm status with counsel.

| Requirement | What good looks like | What to ask a vendor |
|---|---|---|
| Business Associate Agreement | Signed with the vendor, with subprocessors such as the model provider and cloud covered. | Who signs, which products and plans are covered, and what is excluded. |
| No training on your data | Prompts and PHI are not used to train models, with stated retention and, where offered, zero data retention. | How long data is kept and who can read it. |
| Technical safeguards | Encryption in transit and at rest, role-based access, multi-factor authentication. | Which are on by default and which are paid add-ons. |
| PHI detection or redaction | Identifiers detected and removed or masked before processing. | Which identifiers, and whether it blocks or only alerts. |
| Audit trail | Logs of who and which agent accessed what, exportable for review. | Whether logs are default, on request or Enterprise-only. |
| Minimum necessary | Users and agents see only the PHI a task needs. | How permissions inherit from your EHR and identity provider. |
How we assessed: we read each vendor’s own pages and press coverage, and say where a page was vendor-authored, self-ranking or unreachable. Nearly all sources are vendor material. “Not described” means not found on the pages we reviewed, not that the capability is absent. Madison and Opencontroller are our products and are listed first for that reason. This is not legal advice.
The best AI security and HIPAA compliance platforms at a glance
| # | Platform | Best for | Layer | Watch for |
|---|---|---|---|---|
| 1 | Madison by Lyzr | A signed rule-to-evidence record for regulated institutions | Proof | Built for US banks; HIPAA not a described module |
| 2 | Opencontroller by Lyzr | Per-call policy, discovery and signed audit trail for AI agents | Govern | No PHI redaction described; confirm BAA position |
| 3 | BastionGPT | A clinician AI assistant with a BAA on its plans | Assistant | HITRUST and SOC 2 described as in progress |
| 4 | Google Gemini for healthcare | Read-only record access in Epic and Oracle Health | Assistant | US preview; no BAA stated on its page |
| 5 | Nightfall AI | Detecting and redacting PHI across SaaS, AI tools and MCP | Data protection | BAA and certifications not stated on pages read |
| 6 | Fini | Patient support with PII redaction before the model | Patient-facing | Self-published rankings; BAA wording differs by guide |
| 7 | Iternal AirgapAI | Local, on-premises AI for staff | Local | Page says a BAA “may not apply”; claims unsourced |
| 8 | Kore.ai, Talkdesk, Hyro | High-volume patient access and scheduling | Patient-facing | No BAA statement on pages read |
Madison by Lyzr
Madison is a workforce of AI agents for compliance and risk in US banks and credit unions. It reads the rules, your policy and procedure library and your examination history, builds a live map of how they connect, and hands finished, sourced work to a named person who decides.
We list Madison first because every platform below leaves the same gap: someone must show which requirement a control satisfies and who approved it. Madison holds that chain: regulation, rule section, obligation, applicability, policy, procedure, control, test, finding, remediation, evidence and request. Vendors, models and agents are governed objects with owners and evidence, so a BAA, a vendor report or an audit export becomes evidence on the control it supports. Be clear about scope, though: Madison’s live modules cover US banking regulation, it reads from a bank’s systems and does not connect to EHRs, and HIPAA is not a described Madison module. The pattern fits a healthcare organization that wants the same record, but confirm with Lyzr what is supported before you plan around it.

| Governance question | What Madison adds |
|---|---|
| Which AI vendors and agents are in use? | Holds vendors, models and agents as governed objects with owners and evidence. See AI agent inventory for banks. |
| Which requirement does this control satisfy? | Traces the control back through policy and obligation to the rule text. |
| Is there a policy and a control for each obligation? | Flags an obligation with no policy, a policy covering nothing, or an obligation with a policy but no control. |
| Who approved it, and on which version? | Signs every decision against the exact version, with the signer’s role. |
| Can we answer a reviewer’s request? | Answers requests from the chain behind them, in one register. See how to map policies to controls with an agent. |

Best for: regulated institutions that want a signed record behind their AI controls, and banks and credit unions in particular. See AI in compliance vs AI governance and what regulators ask banks about AI agents. Start with a Madison working session.
2. Opencontroller by Lyzr
Best for: governing what AI agents can reach and do, with a signed record of every call.
Opencontroller is Lyzr’s agent control plane. Each agent gets an immutable ID and a named owner. A gateway enforces egress policy per agent and applies budgets that refuse calls once spent. Each tool call is authorized by policy that reads the call’s arguments, so a rule can depend on what is being requested, and credentials are brokered so the agent never holds them. Approvals cover publish, modify, disable and retire, with the approver never the requester. A signed audit trail records lifecycle events, model calls and tool executions, and a reversible quarantine refuses an agent’s calls without a redeploy. It discovers agents across clouds, clusters and devices, including unsanctioned AI clients and MCP configurations, and it runs in the customer’s cloud account.
Where it fits
It addresses the agent side of PHI access: who an agent acts for, what it may call, and a record of what it did. See best platforms for AI agent safety in regulated industries.
What to check
The Capability Reference does not describe PHI detection or redaction, EHR connectors or a BAA. A gateway also governs only traffic that passes through it. Ask Lyzr about its HIPAA position and whether it will sign a BAA before putting PHI near it.
Pick it if: you run your own AI agents and need per-call policy, separated approvals and an audit trail around them.
3. BastionGPT
Best for: a clinician-facing AI assistant that includes a BAA.
BastionGPT, from FortaTech Security LLC, describes a HIPAA-compliant AI assistant with an AI medical scribe, clinical note templates and document analysis, offering the latest GPT, Claude and Gemini models. Its medical page says the BAA is included on all plans, while its security page says every paid plan, and the FAQ says it is accepted automatically when the trial starts. It states customer data is not used for model training, that uploads are wiped after 30 days by default, TLS 1.2 or higher in transit, AES-256 at rest, multi-factor authentication on every plan and audit logs on request. Plans are listed at $20, $45 and $75 per user per month.

Pick it if: you want a clinician assistant with a BAA and are comfortable with SaaS.
Sources: BastionGPT medical page and security page (undated, 2026), and its Claude comparison page. Vendor-authored.
4. Google Gemini for healthcare
Best for: health systems and payers that want an agent reading records in Epic and Oracle Health.
Google’s page describes a Gemini agent with healthcare skills such as record synthesis, appointment preparation, prior authorization and utilization review, with connectors that inherit user permissions. It lists read-only Epic access through FHIR R4 and read-only Oracle Health access, Cloud Audit Logs, VPC Service Controls and customer-managed encryption keys, and says PHI and enterprise prompts are never used to train Google foundation models. A Futurum analysis dated November 10, 2026 reports 27 connectors, named launch customers including HCA and Northwell, and no pricing, accuracy or production results.

Pick it if: you are on Google Cloud and Epic or Oracle Health and will confirm the BAA and preview terms.
Sources: Google Cloud Gemini for healthcare page (undated) and Futurum (November 10, 2026). Vendor-authored and analyst.
5. Nightfall AI
Best for: detecting and redacting PHI as it moves through SaaS, endpoints, AI tools and MCP.
Nightfall’s HIPAA page says it detects HIPAA-defined PHI across more than 100 file types, including images, with alerts and redaction. A September 1, 2026 blog adds AI surfaces, including ChatGPT, Claude, Copilot, IDE agents and MCP, shadow AI discovery, and actions such as block, coach, redact, delete, revoke, quarantine and encrypt across supported channels. Deployment is SaaS connectors plus an endpoint agent. We covered Nightfall in more depth in our data privacy platforms guide for banks.

Pick it if: your first risk is PHI leaving through AI tools and collaboration apps.
Sources: Nightfall HIPAA page (undated) and healthcare DLP blog (September 1, 2026). Vendor-authored.
6. Fini
Best for: patient support where an agent answers questions and takes EHR actions.
Fini’s guides, updated October 30 and November 10, 2026, say PII redaction strips ePHI before it reaches the model, scanning for the 18 HIPAA identifiers and logging redactions for audit, across voice, chat and email, with EHR actions through SMART on FHIR per an FAQ. They list SOC 2 Type II, ISO 27001, PCI DSS Level 1, GDPR, CCPA and HIPAA, and name Rugiet Health, Elation Health and Anima Health.

Pick it if: patient support is your first agent use case and you will verify the BAA and reports.
Sources: Fini guides (October 30 and November 10, 2026). Vendor-authored, self-ranking.
7. Iternal AirgapAI
Best for: running AI locally on your own hardware, without sending data to a public cloud.
Iternal’s healthcare page, updated September 5, 2026, describes AirgapAI as a family of on-premises products, including local chat, transcription and code tools, running on your own hardware, with perpetual licensing from $697 per user. It lists clinical documentation, transcription and an AI receptionist as uses, and says PHI never leaves your network.

Pick it if: you want a locally run assistant and have the hardware and security staff to run it.
Source: Iternal healthcare page (September 5, 2026). Vendor-authored.
8. Kore.ai, Talkdesk and Hyro
Best for: high-volume patient access, scheduling and call handling.
Kore.ai’s provider page describes scheduling, prescriptions, lab results and prior authorization use cases, lists HIPAA, SOC 2, ISO 27001, FedRAMP, GDPR and PCI DSS logos without dates, and names guardrails only generically. Talkdesk’s page calls its Healthcare Experience Cloud HIPAA compliant, says it works with cloud or on-premises contact centers, and its March 2025 launch release covers scheduling, benefits and refill agents with an example prompt that accesses account information via Epic. Hyro’s page describes Epic-integrated assistants for patient verification and scheduling, set up through Epic’s vendor marketplace.

Pick it if: you run a contact center or scheduling at scale and will request each vendor’s BAA and reports.
Sources: Kore.ai, Talkdesk and Hyro pages, Talkdesk release (March 3, 2025) and a third-party Hyro listing. Mostly vendor-authored
What does this guide leave out?
The overview we started from covers assistants, patient-facing agents and data protection. Other guides we read cover categories we did not assess here, and every one of them is vendor-authored. AI scribes: Microsoft’s Dragon Copilot, Ambience, Nabla, Nuance DAX and Upheal appear in vendor guides, and a scribe handles the most PHI per visit, so assess one separately. Voice AI platforms: ElevenLabs, Synthflow, PolyAI, Vapi, Retell and Bland are compared in a Bland guide that says some BAAs apply only when a setting is on, for example ElevenLabs only with zero retention mode and Synthflow only with its HIPAA setting, and that Vapi’s HIPAA mode and zero data retention are mutually exclusive. Those are competitor claims, so verify them. No-code builders: HIPAA Vault’s guide says a builder is not safe for PHI without a BAA, and it does not confirm that Bubble, FlutterFlow or AppSheet sign one. See best tools for voice AI guardrails and compliance for the voice AI pattern in banking.
What is the BAA chain, and what does it not cover?
A Business Associate Agreement is the contract that lets a vendor handle PHI for you. The chain matters because most AI products sit on top of other providers: the assistant vendor, the model provider and the cloud. A BAA with one link does not automatically cover the rest, and a signed BAA is not evidence that safeguards work. Some BAAs also do not cover every model or deployment option, and some apply only when a setting such as zero retention is switched on, so ask whether yours is conditional. That is why the record of who approved the vendor, which products were in scope and what evidence you hold matters as much as the contract. See what regulators ask banks about AI agents for the same question from a banking supervisor.

How do the AI security and HIPAA platforms compare?
| Platform | BAA stated | PHI detection or redaction | Training and retention | EHR access | Deployment | Certifications named | Audit record |
|---|---|---|---|---|---|---|---|
| Madison | Not applicable: confirm with Lyzr | No | Not applicable | No: reads bank systems | Your tenancy: cloud, on-premises or air-gapped | Not quoted here | Signed decisions |
| Opencontroller | Confirm with Lyzr | Not described | Not applicable | No | Customer’s cloud account | Not quoted here | Signed audit trail |
| BastionGPT | Yes: all plans or every paid plan | Not described | No training; uploads wiped after 30 days by default | Copy-paste only | SaaS; Ultra: your enterprise cloud | Badges; HITRUST and SOC 2 in progress | Logs on request |
| Gemini for healthcare | Not mentioned | Not described | Not used to train; retention not stated | Epic, Oracle Health: read-only | Google Cloud; US preview | None named | Cloud Audit Logs |
| Nightfall | Not mentioned | Detects and redacts; other actions by channel | Not described | No | SaaS connectors, endpoint agent | None named or dated | Alerts to SIEM |
| Fini | Differs by guide | Redaction before model | Not described | SMART on FHIR (FAQ) | Cloud | Claimed, undated | Redactions logged |
| AirgapAI | Says it “may not apply” | Not described | Local to your network | Not described | On-premises or private cloud | None; page says no AI product is HIPAA certified | General |
| Kore.ai, Talkdesk, Hyro | Not stated on pages read | Hyro: third-party listing only | Not described | Epic (Hyro, Talkdesk example), others | Cloud; Talkdesk also on-premises contact centers | Undated logos | Not described |
Based on the pages and sources named in each entry. “Not described” means not found on the pages we reviewed, not that the capability is absent. Many cells are vendor claims.
How do you choose an AI platform for HIPAA compliance?
Step 1: List where PHI meets AIName each assistant, agent, vendor and employee tool that could touch PHI. See AI agent inventory for the method.
Step 2: Get the BAA scope in writingAsk who signs, which plans and features are covered, and whether the model provider and cloud are covered.
Step 3: Decide where PHI is removedChoose whether redaction happens before the model, at the endpoint or not at all, and who owns it.
Step 4: Apply minimum necessary to agentsGive each agent its own identity and the narrowest access it needs. See best platforms for AI agent safety.
Step 5: Collect the evidenceAsk for reports with scope and dates, and export logs you can read. See platforms for AI data privacy compliance.
Step 6: Keep the approval on recordHold requirement, policy, control, vendor evidence and sign-off in one record, ready for an auditor or investigator.
| Question to ask a vendor | Why it matters |
|---|---|
| Will you sign a BAA, and does it cover subprocessors? | PHI may pass through the model provider and cloud. |
| Which plans and features are excluded from the BAA? | Some features may sit outside coverage. |
| Does the BAA depend on a setting, such as zero retention or a HIPAA mode? | Coverage can switch off if the setting is off. |
| How long are prompts and files retained, and who can read them? | Retention is part of your risk analysis. |
| Does redaction run before the model, and which identifiers? | Redaction placement determines what the model sees. |
| Do agents get their own identity and logs? | Shared accounts weaken access control and audit. |
| Which reports can you share, and what do they cover? | Certificates cover named products and dates. |
If your gap is the governance record, talk to us about Madison or Opencontroller, and read the AI governance glossary. For related guides see AI agent observability and voice AI guardrails.
Bring your AI vendor list and your policies
Book a working session to see where your controls, vendors and obligations connect, and what scope fits your organization.
Book A Demo: Click Here
Join our Slack: Click Here
Link to our GitHub: Click Here
Got a use case in mind?
8 weeks from use case to agents running in production.
Platform, people and FDEs, all in. Bring your environment. We'll co-build and stay until it's live.
Talk to UsFree resource
101 AI Agents Use Cases
100+ production-ready AI agent use cases across Marketing, Sales, HR, Banking, Insurance, Operations and a lot more
Download now