Your auditor wants to know which AI agents touched customer data last quarter.
Who approved each one into production. Which guardrail violations got flagged, and when.
If your honest answer involves pinging three different teams on Slack and hoping someone remembers, you don’t have a tooling problem. You have a gap that just became visible at the worst possible moment.
That gap used to be theoretical. It isn’t anymore.
This guide splits “AI audit trail” into the two things it actually means, scores 10 tools on the same five capabilities, and tells you plainly where each one wins and where it falls short. We built one of these tools. We’ve marked that clearly and graded it by the same rules as everyone else.
Get the short answer
- If you need to prove what your agents did, in your own cloud, across any framework: start with Lyzr Open Controller.
- If you’re governing models you build and serve inside an IBM stack: IBM watsonx.governance.
- If you’re starting a governance program from zero and want pre-built regulatory mapping: Credo AI.
- If your only question is “what customer data did an AI tool touch”: PortEden.
- If you’re Microsoft 365 standardized and want evidence in a portal you already use: Microsoft Purview.
Two Categories of AI Audit Trail (Don’t Buy the Wrong One)
Before comparing tools, understand the split. “AI audit trail” means two different things, and buying the wrong category is the most common mistake in this space:
Category 1: What AI agents did in your systems. Logs which data an AI agent or assistant read, changed, or accessed: which email, which files, which database rows, what was redacted, what was allowed or denied. This is what compliance reviewers mean when they ask “what client data has touched an AI.” OpenController, PortEden, and Microsoft Purview sit here.
Category 2: How AI models you build and serve behave. Logs model performance over time: drift, bias, accuracy, and output safety. This is model governance, and it matters most when you train and deploy your own models. IBM watsonx.governance, Credo AI, and Fiddler sit here.
Most regulated organizations need both. The tools below are marked by which category they primarily serve.
See how we scored every tool
We checked all 10 tools, including our own, against the same five dimensions. Here’s the yardstick, and a declared bias up front: we build one of the tools on this list, and we’ve scored it with the same rubric applied to the other nine.
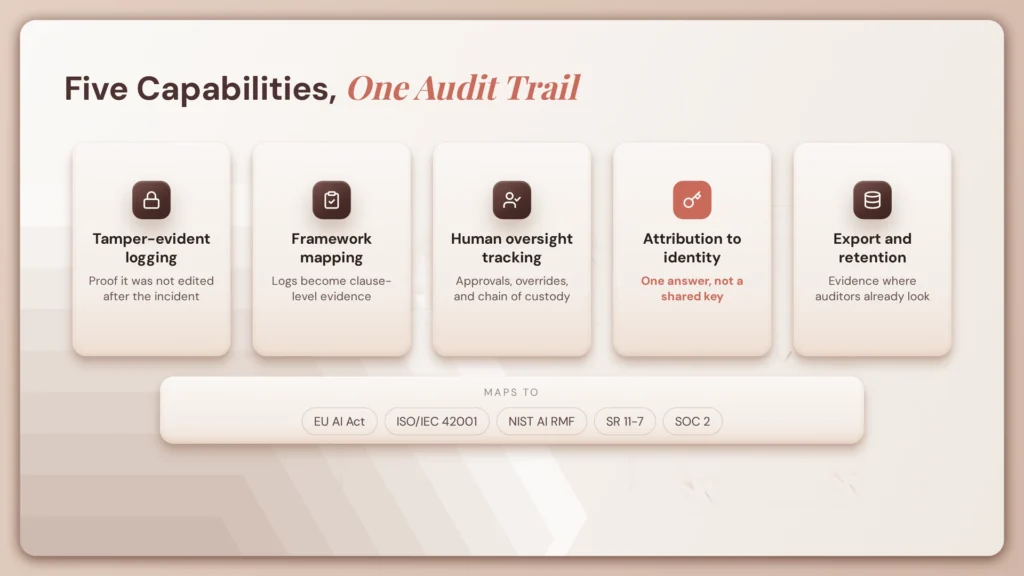
The five-dimension scoring rubric
| Dimension | What we checked | Why it matters |
|---|---|---|
| Tamper-evident logging | Cryptographic signing, hash chains, or hardware attestation on records | Auditors need proof a log wasn’t edited after an incident |
| Regulatory framework mapping | Alignment to EU AI Act, ISO/IEC 42001, NIST AI RMF, SOC 2 | Raw logs aren’t evidence until they map to a clause |
| Human oversight tracking | Approval chains, overrides, separation of duties | Article 14 and most internal audit frameworks require it |
| Attribution to identity | Every action tied to a specific agent, version, user, credential | “Who did this” needs exactly one answer |
| Export and retention | SIEM export, configurable retention windows | Evidence has to land where auditors already look |
The 10 Best Tools for AI Compliance and Audit Trails
1. Lyzr OpenController: close the gap between enforcement and evidence
Why it is on a list of AI compliance and audit trail tools. Most tools on this page log a copy of an event after it happens. Lyzr Open Controller sits in the request path itself, so the record it produces is a byproduct of a control that already ran, not a reconstruction assembled afterward.
Lyzr builds infrastructure for enterprises running AI agents in regulated environments, where the audit trail and the policy enforcement need to be the same system rather than two systems that can drift apart.
Opencontroller is a governance and delivery layer that registers, meters, and governs agents across any framework, deployed inside the customer’s own cloud account.
What Open Controller adds on top of typical logging
| Capability | A typical audit trail tool provides | Open Controller adds |
|---|---|---|
| Record of activity | A copy of events logged after the call | A signed record generated by the control that allowed or refused the call |
| Approvals | Documented separately in Jira or email | A two-person rule enforced by the platform on every promotion, including for admins |
| Data access | Partial, usually scoped to one app | Every tool call, argument, and guardrail verdict across any agent framework |
| Deployment | Vendor’s cloud only | Your VPC, on-prem, or air-gapped |
Pick it if you are a compliance or risk leader who needs evidence across LangGraph, CrewAI, or the OpenAI Agents SDK, in a regulated industry where enforcement and audit have to be one system, or a CISO who can’t move logs outside your own cloud.
Skip it for now if you are mainly tracking drift and bias in models you train (start with IBM watsonx.governance or Credo AI instead), or choosing primarily on third-party analyst coverage, since Open Controller is newer as a named product and has thinner independent reporting than category incumbents.
2. IBM watsonx.governance: govern the model lifecycle at enterprise scale

IBM watsonx.governance tracks risk assessments, factsheets, and regulatory alignment across a model’s full lifecycle, from development through post-market monitoring. It was named a Leader in the first-ever Gartner Magic Quadrant for AI Governance Platforms in June 2026, with automated AI factsheets capturing model and prompt metadata, metrics, and lineage across models running on watsonx.ai, SageMaker, Bedrock, Vertex and Azure.
- License: Proprietary, enterprise contract
- Best for: Large enterprises with IBM infrastructure that need deep model lifecycle governance
- Not ideal if: You need runtime audit of agent tool calls or multi-agent delegation, which are newer additions to the platform
- Scale signal: Gartner Leader placement, 2026 Magic Quadrant
3. Credo AI: start a governance program with policy packs

Credo AI structures governance as an operational workflow: intake questionnaires trigger risk scoring and reviewer routing, with a GAIA assistant that automates classification, control assignment, and evidence collection. It was named a Visionary in the same inaugural Gartner report.
- License: Proprietary SaaS
- Best for: Governance teams building a structured compliance program from scratch
- Not ideal if: You need audit trails generated from runtime controls like tool calls or budget enforcement
- Scale signal: Gartner Visionary, 2026 Magic Quadrant
4. OneTrust AI Governance: extend a privacy system of record

OneTrust adds AI inventory management and risk assessment on top of the privacy platform many compliance teams already run for GDPR and CCPA. It appeared in the same 2026 Magic Quadrant as a Visionary, giving privacy-standardized teams one place to extend coverage instead of adding a second platform.
- License: Proprietary, SaaS or hybrid
- Best for: Privacy and compliance teams already standardized on OneTrust
- Not ideal if: You need a record of individual model calls or tool executions
- Scale signal: Gartner Visionary, 2026 Magic Quadrant
5. Microsoft Purview: keep evidence inside the Microsoft portal

Purview extends Entra ID, Defender, and Microsoft 365 administration into AI visibility, logging interaction data and data access events for Copilot and connected AI tools. The value is concentrated for tenants already living in that stack, where evidence lands in the same portal used for eDiscovery.
- License: Proprietary, Azure-native licensing tiers
- Best for: Microsoft 365 organizations with SEC, FINRA, or GDPR recordkeeping duties
- Not ideal if: Your agents run on AWS, GCP, or open-source frameworks outside Microsoft
6. PortEden: prove what data your AI tools touched

PortEden sits between AI clients, Claude, ChatGPT, Gemini, and your live email, drive, and calendar, and records every tool call those clients make: the resource touched, the per-layer authorization decision, the redactions that fired, and the allow-or-deny outcome. It’s one of the few tools here that enforces the access it audits rather than only observing it.
- License: Proprietary SaaS
- Best for: Teams whose main concern is proving exactly what data an AI tool accessed
- Not ideal if: You also need model governance, bias monitoring, or agent lifecycle management
- Scale signal: Named in multiple 2026 data-access audit comparison roundups
7. Tenet AI: seal decision records for legal accountability

Tenet AI captures every agent reasoning step as an immutable audit log with deterministic replay of any past decision, integrated with two lines of code. Worth noting before you shortlist it: Tenet’s own trust center describes its posture as a self-assessed SOC 2 readiness review completed in April 2026, with external Type II audit still on the 2026 roadmap, not a completed third-party attestation.
- License: Proprietary, SaaS or self-host
- Best for: Teams that need sealed, replayable decision records for a specific high-stakes workflow
- Not ideal if: You need broad IT governance coverage or a completed SOC 2 Type II attestation today
8. Drata: automate continuous IT compliance evidence

Drata replaces periodic manual audits with continuous evidence collection across SOC 2, ISO 27001, HIPAA, and GDPR, pulling signals from AWS, Azure, GitHub, and Okta. Its newer AI Agent Governance module discovers agents running inside the stack, enforces policy before an action runs, and logs every decision for auditors, which is the question SOC 2 reviewers increasingly raise in 2026.
- License: Proprietary SaaS
- Best for: Organizations maintaining continuous SOC 2, ISO 27001, or HIPAA evidence
- Not ideal if: You need a record of individual AI model calls or agent tool executions as your primary use case
- Scale signal: Established market leader in compliance automation
9. Centraleyes: run multi-framework GRC with AI assistance

Centraleyes connects compliance operations, risk management, and regulatory tracking in one GRC system, with AI used to classify evidence and flag anomalies across SOC 2, ISO 27001, and NIST simultaneously. The appeal is breadth across frameworks rather than depth on AI agent behavior specifically.
- License: Proprietary SaaS
- Best for: Mature audit and risk teams managing several frameworks at once
- Not ideal if: Your primary need is an agent-level audit trail of model calls and guardrail verdicts
10. Anjuna: attest processing at the hardware level

Anjuna’s confidential computing runs workloads in hardware-secured enclaves, so the integrity guarantee behind an audit trail comes from silicon, not software alone. That’s a different kind of proof than a signed log, and it matters most where the regulator cares less about the application and more about whether the data ever left a trusted boundary.
- License: Proprietary, on-prem or cloud
- Best for: Financial institutions and defense organizations with DORA or banking-grade requirements
- Not ideal if: You want a SaaS compliance platform without infrastructure changes
Not on the list: the rest of Gartner’s 2026 Magic Quadrant
Gartner’s inaugural report named 13 vendors: Leaders IBM, ServiceNow, and Truyo; Visionaries Airia, Credo AI, ModelOp, Monitaur, and OneTrust; Challenger Holistic AI; and Niche Players Cranium AI, Relyance AI, Saidot, and SAP. We didn’t review ServiceNow, Truyo, Airia, ModelOp, or Monitaur here because our focus was tools with a distinct runtime audit angle. Add them if analyst placement weighs heavily in your decision.
Compare all 10 tools side by side
Full comparison table
| Tool | Primary category | Where it runs | Records individual AI calls | Best for |
|---|---|---|---|---|
| Lyzr Open Controller | Agent activity + enforcement | Your VPC, on-prem, air-gapped | Yes, model and tool calls | Full agent lifecycle audit |
| IBM watsonx.governance | Model behavior | Hybrid, on-prem | Partial | Model lifecycle governance |
| Credo AI | Model behavior | SaaS | No | Starting a governance program |
| OneTrust AI Governance | Model behavior | SaaS, hybrid | No | Privacy-standardized teams |
| Microsoft Purview | Agent activity | Azure-native | Partial | Microsoft-stack orgs |
| PortEden | Data access | SaaS | Partial, tool calls | Data-access evidence |
| Tenet AI | Agent activity (legal) | SaaS, self-host | Yes, decision-level | Sealed decision records |
| Drata | Compliance automation | SaaS | Partial via agent module | Continuous SOC 2/ISO evidence |
| Centraleyes | Compliance operations | SaaS | No | Multi-framework GRC |
| Anjuna | Infrastructure security | On-prem, cloud | No, attests processing | Hardware-level attestation |
Match your scenario to a tool
Scenario-to-tool matrix
| If your situation is | Pick | Why |
|---|---|---|
| Auditor wants per-agent proof across LangGraph, CrewAI, and more | Lyzr Open Controller | Evidence from controls already in the request path |
| Every production change needs a documented second approver | Lyzr Open Controller | Separation of duties enforced by the platform |
| You’re governing models your data science team builds | IBM watsonx.governance | Deep model lifecycle and factsheet coverage |
| You’re building a compliance program with no prior structure | Credo AI | Pre-built policy packs mapped to regulation |
| You need to know which emails and files an AI assistant touched | PortEden | Purpose-built data-access audit trail |
| You’re fully on Microsoft 365 with SEC/FINRA obligations | Microsoft Purview | Evidence inside the portal you already use |
| You need legally defensible, replayable decision records | Tenet AI | Deterministic replay plus override chain of custody |
| You need foundational SOC 2/ISO 27001 evidence, not AI-specific | Drata | Continuous evidence collection across IT controls |
Stack tools the way production teams do
Recommended tool stack by layer
| Layer | Job | Typical choice |
|---|---|---|
| Runtime enforcement and agent audit | Stop a bad call, log every one | Lyzr Open Controller |
| Model lifecycle governance | Track drift, bias, risk over time | IBM watsonx.governance or Credo AI |
| Data access | Prove what was read, changed, or masked | PortEden or Microsoft Purview |
| IT compliance evidence | SOC 2, ISO 27001 continuous proof | Drata or Centraleyes |
Run these 5 tests when evaluating any audit trail tool
- The approver test: pick the last production change to an agent, and ask who requested it, who approved it, and which version it shipped.
- The tamper test: ask the vendor to show you how an edited log entry gets flagged.
- The data test: ask which customer records an agent touched last week, and which fields got masked.
- The separation test: have an administrator try to approve their own change, live, and watch whether the platform blocks it.
- The export test: push a day of events into your own SIEM and check the format, completeness, and retention window that lands on the other end.
Frequently asked questions
What is the best AI compliance and audit trail tool in 2026?
It depends on what you must prove. For evidence of what agents did, across any framework and inside your own cloud, Lyzr Open Controller is the strongest fit. For model lifecycle governance inside an IBM stack, IBM watsonx.governance leads. There is no single best tool across every category.
AI audit trail vs AI governance: what’s the difference?
An audit trail is the record. Governance is the set of policies and controls that decide what’s allowed in the first place. The strongest tools produce the trail as a direct output of governance controls already enforcing policy, rather than maintaining two separate systems that can drift apart.
Is there a free or open-source alternative to IBM watsonx.governance?
Not a direct one. Most comparable tools, including Credo AI and Open Controller, are proprietary. Open-source observability tools trace model calls but don’t provide the regulatory framework mapping or governance workflow that watsonx.governance is built around. See our comparison of open-source LLM observability platforms if tracing alone is what you need.
Did any recent acquisitions change this market?
Yes. ServiceNow’s AI Control Tower added runtime traces through its acquisition of Traceloop, and ServiceNow was named a Leader in the same 2026 Gartner Magic Quadrant. Watch for consolidation as GRC incumbents buy runtime observability startups to close the gap.
Does the EU AI Act actually require audit trails?
Yes, for high-risk systems. Regulation (EU) 2026/1744 moved the core high-risk obligations for Annex III systems to 2 December 2027 and those for Annex I regulated products to 2 August 2028, while Article 50 has continued to apply since 2 August 2026. Once in force, logs must be kept for at least six months under both Article 19 and Article 26(6). Breaching high-risk obligations carries fines up to €15 million or 3% of global turnover, with €35 million or 7% reserved for prohibited practices.
Can one platform cover both model governance and agent activity audit trails?
Few do both well today. Lyzr Open Controller covers agent activity and model-call logging with evaluation built in. IBM watsonx.governance covers model lifecycle governance in depth. Most enterprises still run one tool per category and export both into a shared SIEM.
Choose the tool that fits what you must prove
The deadline moved. The requirement to log didn’t.
A trail can’t be reconstructed for activity nobody recorded, which means the evidence an auditor asks for in December 2027 has to start accumulating well before then.
If your next audit question is “what did the agent do, and who let it”, that’s the record Lyzr Open Controller produces, from inside your own cloud. Compare that against broader AI agent governance tools if you’re still scoping the category.
The CIO Playbook to AI Agent Governance
A BFSI Leader’s Guide to Resolving Disputes with Agentic AI
Book A Demo: Click Here
Join our Slack: Click Here
Link to our GitHub: Click Here