Agentic AI changes the third line of defense in three ways: audit moves from periodic samples toward continuous testing, evidence has to come from a trail of what each agent did and who approved it, and human judgment stays where it matters most, on materiality, missing context and scope drift. Not every source agrees that full-population testing is the answer, and none we read settled how auditors stay independent when they rely on agents themselves. The audit trail is the dependency for everything else, and you cannot retrofit one. Madison, Lyzr’s agentic GRC product for US banks and credit unions, keeps the record that links rules, policies, controls, approvals and evidence, which is the material auditors test. It is a first and second line system, not an audit tool, and auditors should test it like any other.
TL;DR
- Periodic sampling is a poor fit: KPMG and IIA Singapore say retrospective sample testing is ill-suited to agentic workflows. Richard Chambers, a senior adviser at audit-software vendor Optro, says periodic review is inadequate.
- But “test everything” has a catch: one consulting firm notes that once a trail exists, the audit is still often a sampling exercise. The real shift is evidence captured at decision time.
- Audit the control, not just the output: inventory and ownership, tool permissions, decision records, escalation and override, testing and change management.
- Approval gates can be theatre: a reviewer name and a timestamp look identical whether the review was real or a rubber stamp.
- Judgment stays human: agents can retrieve and test; auditors decide what a finding means.
- Fair warning: most guidance here is vendor or adviser opinion, labelled as such, and we sell Madison.
What changes for the third line when banks deploy AI agents?
The third line gives independent assurance over the first line, which runs the business, and the second line, which sets risk and compliance boundaries. When agents act on their own in first-line workflows, six parts of that job change. The table below states each shift and where the source support is strong or thin. For the wider governance picture see AI in compliance vs AI governance.
| Area | From | To | Support |
|---|---|---|---|
| Testing | Periodic samples of human-led work | More continuous testing of agent behavior between cycles | KPMG and IIA Singapore, Optro (vendor) |
| Evidence | Sign-offs and interviews with decision-makers | A trail of actions, reasons, approval gates and owners | Optro, Lumenova, Arya (vendors) |
| Scope | Process and control design | Also agent identity, permissions and tool reach | KPMG: treat agents as privileged users |
| Reporting | Summaries of isolated snapshots | Whether controls held across the period | Overview-level claim; thin in sources |
| Judgment | Auditor reviews human decisions | Auditor decides what agent exceptions mean | Optro: only humans decide what answers mean |
| Methodology | AI as a bolt-on tool | Methods evolve with first and second line deployment | Overview-level claim; IIA tool names agentic AI as in scope |
“Support” lists the sources we read for each shift. Rows marked overview-level come from the summary this guide started from; we did not find primary support for them. Several sources are vendors.
Does continuous assurance mean testing every transaction?
Not necessarily. KPMG and IIA Singapore call for real-time monitoring over retrospective auditing and say sample testing is ill-suited to agentic workflows. Sphere, a consulting firm, writes that once the trail exists, the audit itself is still a sampling exercise, not a full-population review. Both can be true: the trail has to cover everything, while the auditor may still choose how much to test. What changes is that the population is available, so sampling becomes a choice, not a limit.


What evidence should internal audit ask for on an AI agent?
Lumenova, a governance vendor, lists six areas to audit: inventory and ownership, tools and permissions, decision records, escalation and override, testing, and change management. We use them as a frame, add what KPMG says about agent identity, and set a strong-evidence test and a red flag for each. This is our synthesis, not an audit standard. See AI agent inventory for banks for the inventory step.
| Area | What auditors look at | Strong evidence | Red flag |
|---|---|---|---|
| Inventory and ownership | Every agent, with a named owner before deployment | A register tied to owners, tested against what is actually running | Agents no register knows about |
| Tools and permissions | What each agent can call, read and write, and whose authority it inherits | A permission list matched to actual grants; agents treated as privileged users | Broad shared service accounts |
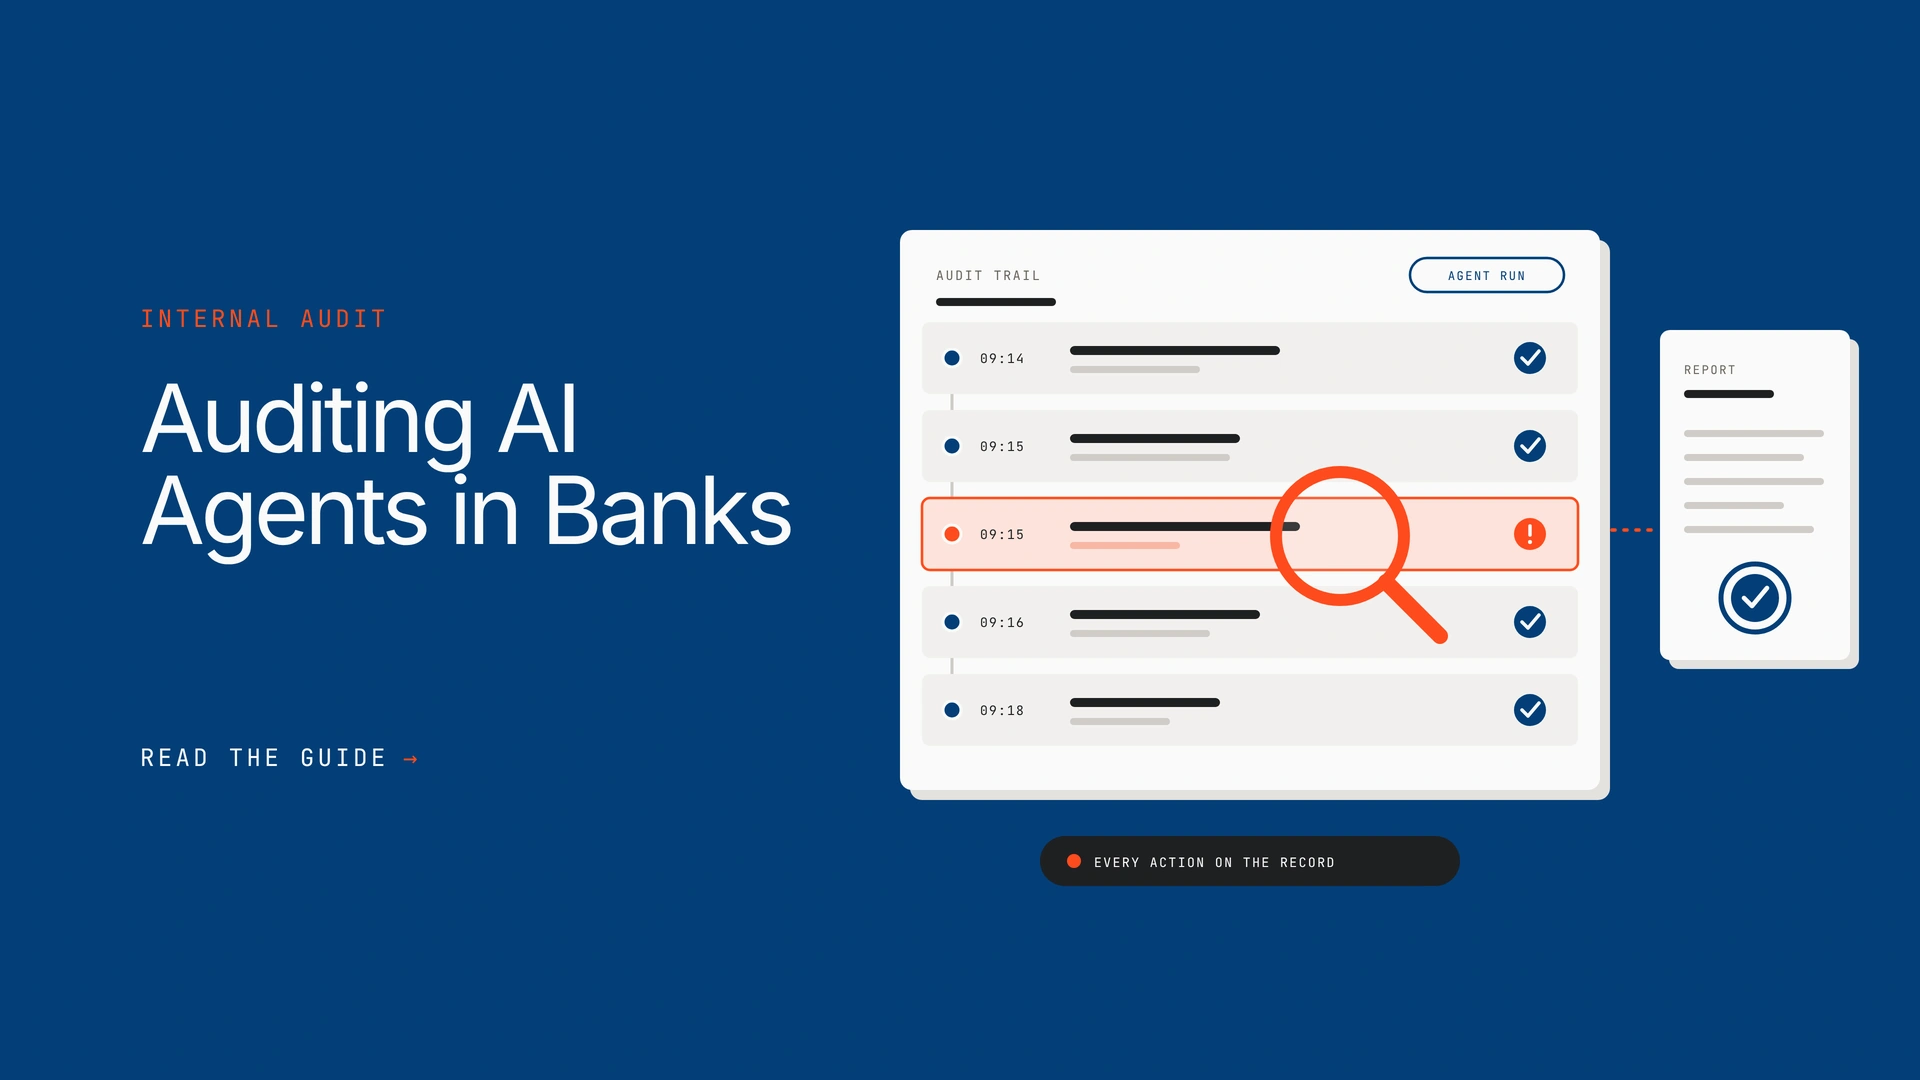
| Decision records | What the agent did, why, which approval gates existed and who owned the outcome | A concise rationale tied to observable evidence and actions, captured at the time | Logs rebuilt after the fact |
| Escalation and override | When the agent hands off and whether humans override it | Override use measured, with a stated reason each time | An override that exists on paper and is never used |
| Testing | How the agent is tested before and after changes | A regression set, adversarial tests and repeated runs | A demo and a single pass |
| Change management | Model, tool, data and rule changes | Revalidation triggered by change; new tools reviewed like new agents | Tools added to live agents with no review |

Where Madison and Opencontroller help: Madison holds vendors, models and agents as governed objects with owners and evidence, and signs each decision against the exact version with the signer’s role. Opencontroller, Lyzr’s agent control plane, keeps a signed audit trail of lifecycle events, model calls and tool executions and applies per-tool authorization. See best tools for AI agent observability in banking.
How do you audit an approval gate that may be a rubber stamp?
Lumenova points out that the evidence looks identical either way: a reviewer name, a timestamp and an approval. Sphere describes the same pattern, with one approver clearing hundreds of gates a day with no rejections, and notes its worked examples are illustrative. The audit step is therefore to test the gate, not just confirm it exists.
| Test | What to measure | Why it matters |
|---|---|---|
| Rejection rate | How often approvers reject, send back or edit | Zero rejections across hundreds of gates suggests no real review |
| Time and volume per approver | Gates cleared per person per day, and time spent | Volume beyond human review capacity makes the gate a bottleneck or a stamp |
| Separation | Whether the approver is ever the requester | A gate the requester can clear is not a gate |
| Override reasons | Whether overrides carry a stated reason | Attributable decisions let you reconstruct judgment |
| Scope check | Whether the action was within the originating request | Scope drift passes unless the gate checks it |
See what a bank board needs to see before approving an AI agent for the intervention points the board should expect, and why bank-built compliance agents stall on review queues that break under volume.
What stays with the human auditor when agents do part of the work?
Agents can execute structured, rule-based tasks such as retrieving evidence or running a control test on a defined step. Richard Chambers, in a post for audit software vendor Optro, argues that accountability must tie back to humans and that only humans decide which questions matter and what the answers mean. Sphere says agent audits still need a human tester. An exception’s severity, the context a dataset lacks and a drift in scope are judgment calls.

Agents also change on their own. Lumenova notes agents can change behavior without any code change, and that adding a tool to an existing agent rarely triggers the review a new agent would get. Audit plans should treat a change in model, tool or data as a trigger for fresh testing.
Who owns what across the three lines when agents are involved?
Agents sit in the first line, boundaries sit in the second and assurance sits in the third. The risk is a blur: a team that builds the agent also approves its own limits. A clear split also tells audit what to test.

| Line | Responsibility for agents | What audit tests |
|---|---|---|
| First: operations and technology | Deploys the agent, names its owner, operates day-to-day controls | Whether controls operated, and whether the trail exists |
| Second: risk and compliance | Sets boundaries, tiers, approval rules and policy; monitors | Whether the framework exists, is current and is applied |
| Third: internal audit | Independent assurance, reporting to the audit committee | Own testing, own evidence, and its own use of agents |
KPMG’s playbook advises verifying whether the organisation has an AI governance framework at all before evaluating technical accuracy. See how to map policies to controls with an agent.
What do standards and regulators say about auditing AI agents?
No US supervisor has issued audit-specific rules for AI agents that we found. What exists is professional guidance and the wider supervisory picture, summarized below. See SR 26-2 and the banking AI governance gap and what regulators ask banks about AI agents.
| Source | What it says | Status |
|---|---|---|
| The IIA: Auditing AI in Banking Organizations (November 3, 2026) | A tool built with input from 12 global banking organizations, with six pillars: governance and policy, risk taxonomy and assessment, model risk management, technology and cybersecurity, operational resilience and third-party management, and talent and AI literacy; covers generative and agentic AI | Members-only download; we read only the public description |
| KPMG and IIA Singapore (2026) | Real-time monitoring over retrospective audit; agent-initiated actions logged and reviewed; agents as privileged users; audit committee reporting beyond technical metrics | Professional-services playbook; not a standard |
| Deloitte hot topics 2026, via GRC Report | Agentic AI a “mega hot topic” for internal audit; continuous scoping; internal audit as an operating system for integrated assurance | Secondary summary; Deloitte report not read |
| SR 26-2 (April 17, 2026) | Generative and agentic AI placed outside the guidance scope; banks govern them through their own risk management | Supervisory guidance; verify against the primary text |
We did not read the IIA tool itself, so we cannot say what it recommends on audit trails or approval gates. This is not legal advice.
What should internal audit report to the audit committee?
The overview this guide started from says reporting should shift toward whether controls held continuously across the period. KPMG’s playbook says the audit committee should receive reporting beyond technical factors such as uptime, though the passage we could read was cut short. We suggest five items, our own synthesis.
| Report item | What the committee learns |
|---|---|
| Coverage of the agent inventory | How many agents exist, how many have owners, how many were tested |
| Control operation across the period | Whether limits and approvals held, with exceptions and trends |
| Gate quality | Rejection, override and volume measures from the gate tests |
| Trail completeness | Whether a real decision could be reconstructed, with failures noted |
| Open findings and age | Findings tied to remediation and the owner, with dates |
What about independence when the auditor relies on agents too?
None of the sources we could read addressed this directly. Our view: treat the audit agent as a tool under audit rules, keep its prompts, scope and outputs reviewable, and keep a named human accountable for each conclusion. Independence also means testing the second line’s evidence, not just consuming it. If the bank’s compliance record is the main source for a test, the auditor should still pick items and check them against the underlying systems. This is a gap in the guidance, so raise it with your chief audit executive and counsel.
How do you adapt the internal audit plan for AI agents?
Step 1: Get the inventoryObtain the list of agents, owners and reach, and test it against what is running. See AI agent inventory for banks.
Step 2: Tier the work by riskScale scope and rigor with risk, data sensitivity and workflow complexity, and start with the highest-risk workflows.
Step 3: Run the replay testPick real decisions and ask the team to rebuild them from the trail, without help from the people involved.
Step 4: Test the gatesMeasure rejection, volume, separation and override reasons, not just whether a gate exists.
Step 5: Set change triggersRe-test when a model, tool, data source or rule changes, and review new tools like new agents.
Step 6: Report and upskillReport the five items to the audit committee and build AI skills in the team. The IIA article on upskilling says required learning speeds the curve more than optional learning.
How does Madison help the first and second lines give auditors better evidence?
Madison is a workforce of AI agents for compliance and risk in US banks and credit unions. It connects regulation, rule section, obligation, policy, procedure, control, test, finding, remediation and evidence in one model, with agents proposing and a named person approving. Each decision is signed against the exact version with the signer’s role, outputs trace to rule text, and gaps such as an obligation with no policy or a policy with no control are flagged. It also holds vendors, models and agents as governed objects with owners and evidence. That is the material an auditor samples and tests.

Pair it with Opencontroller: Opencontroller supplies runtime facts: immutable agent IDs, enforced limits, a signed audit trail and reversible quarantine. A gateway governs only the traffic that passes through it. Descriptions of both products come from Lyzr’s own materials. See also best platforms for AI agent safety in regulated industries.
Walk the replay test with your own data
Bring one agent and one real decision. In a working session we trace it through the record and list what an auditor would still ask for.
Frequently asked questions
How does agentic AI change bank internal audit?
It pushes the third line from periodic samples of human-led work toward continuous testing of agent behavior, evidence drawn from a trail of actions, reasons, approvals and owners, and scope that includes agent identity and tool reach. Human judgment stays with the auditor. Several sources are vendors, so treat the specifics as guidance, not standards.
What is the third line of defense in a bank?
Internal audit. The first line runs the business and operates controls, the second line, risk and compliance, sets boundaries and monitors, and the third line gives independent assurance to the board and audit committee. With AI agents, the third line tests both of the others instead of relying on them.
What is continuous auditing for AI agents?
It means testing agent behavior between audit cycles, often on the full population of actions instead of a sample. KPMG and IIA Singapore say retrospective sample testing is ill-suited to agentic workflows. It depends on a trail captured at decision time, because a trail cannot be rebuilt afterwards.
Can internal audit still use sampling for AI agents?
Yes. Sphere, a consulting firm, notes that once a trail exists the audit is still a sampling exercise, not a full-population review. What changes is that the full population is available, so sampling becomes a choice. Auditors still decide how much to test, based on risk.
What evidence should auditors ask for on an AI agent?
Ask for the agent inventory with owners, the permission list, decision records with rationale and approvals, escalation and override data, test results with a regression set, and change records for models, tools and data. Lumenova, a governance vendor, frames these as six audit areas. Test them against what is actually running.
How do you audit an AI agent’s approval gate?
Test the gate, not just its existence. Measure rejection rate, volume and time per approver, whether the approver is ever the requester, whether overrides carry a reason and whether the action stayed within the original request. A reviewer name and timestamp look the same whether the review was real or a rubber stamp.
What is scope drift in an AI agent?
It is an agent acting outside the scope of the request that started it, for example a review agent beginning to touch decisions it was never meant to make. Sphere describes actions outside the originating request as an audit concern. Auditors check scope at the gate and in the decision record.
What stays with the human auditor when agents help?
Judgment. Agents can retrieve evidence and run rule-based tests on defined steps, but people decide whether an exception is a minor gap or a material weakness, what the data does not show and which questions matter. Optro’s Richard Chambers argues that accountability must tie back to humans.
What does the IIA say about auditing AI in banks?
On November 3, 2026 the IIA published Auditing AI in Banking Organizations, a members-only tool developed with input from 12 global banks, with six pillars and coverage of generative and agentic AI. We read only the public description, so we cannot say what it recommends on audit trails or gates.
What should internal audit report to the audit committee about AI agents?
We suggest agent inventory coverage, control operation across the period, gate quality measures, trail completeness and open findings with age. KPMG’s playbook says committee reporting should go beyond technical measures such as uptime. This list is our synthesis, not a standard.
How can auditors stay independent if they use AI agents?
The sources we read did not address this. Our view is to treat an audit agent as a tool under audit rules, keep its scope and outputs reviewable, keep a named human accountable for each conclusion and test the second line’s evidence against underlying systems. Raise it with your chief audit executive and counsel.
How does Madison help internal audit?
Madison, Lyzr’s agentic GRC product for US banks and credit unions, is a first and second line system. It links regulations, policies, controls, tests, findings and evidence, signs decisions with the signer’s role and holds agents as governed objects with owners. Auditors can sample it, but should test it independently. We have not confirmed workpaper features.
Book A Demo: Click Here
Join our Slack: Click Here
Link to our GitHub: Click Here
Got a use case in mind?
8 weeks from use case to agents running in production.
Platform, people and FDEs, all in. Bring your environment. We'll co-build and stay until it's live.
Talk to UsFree resource
101 AI Agents Use Cases
100+ production-ready AI agent use cases across Marketing, Sales, HR, Banking, Insurance, Operations and a lot more
Download now