A control plane can't govern what it can't see.
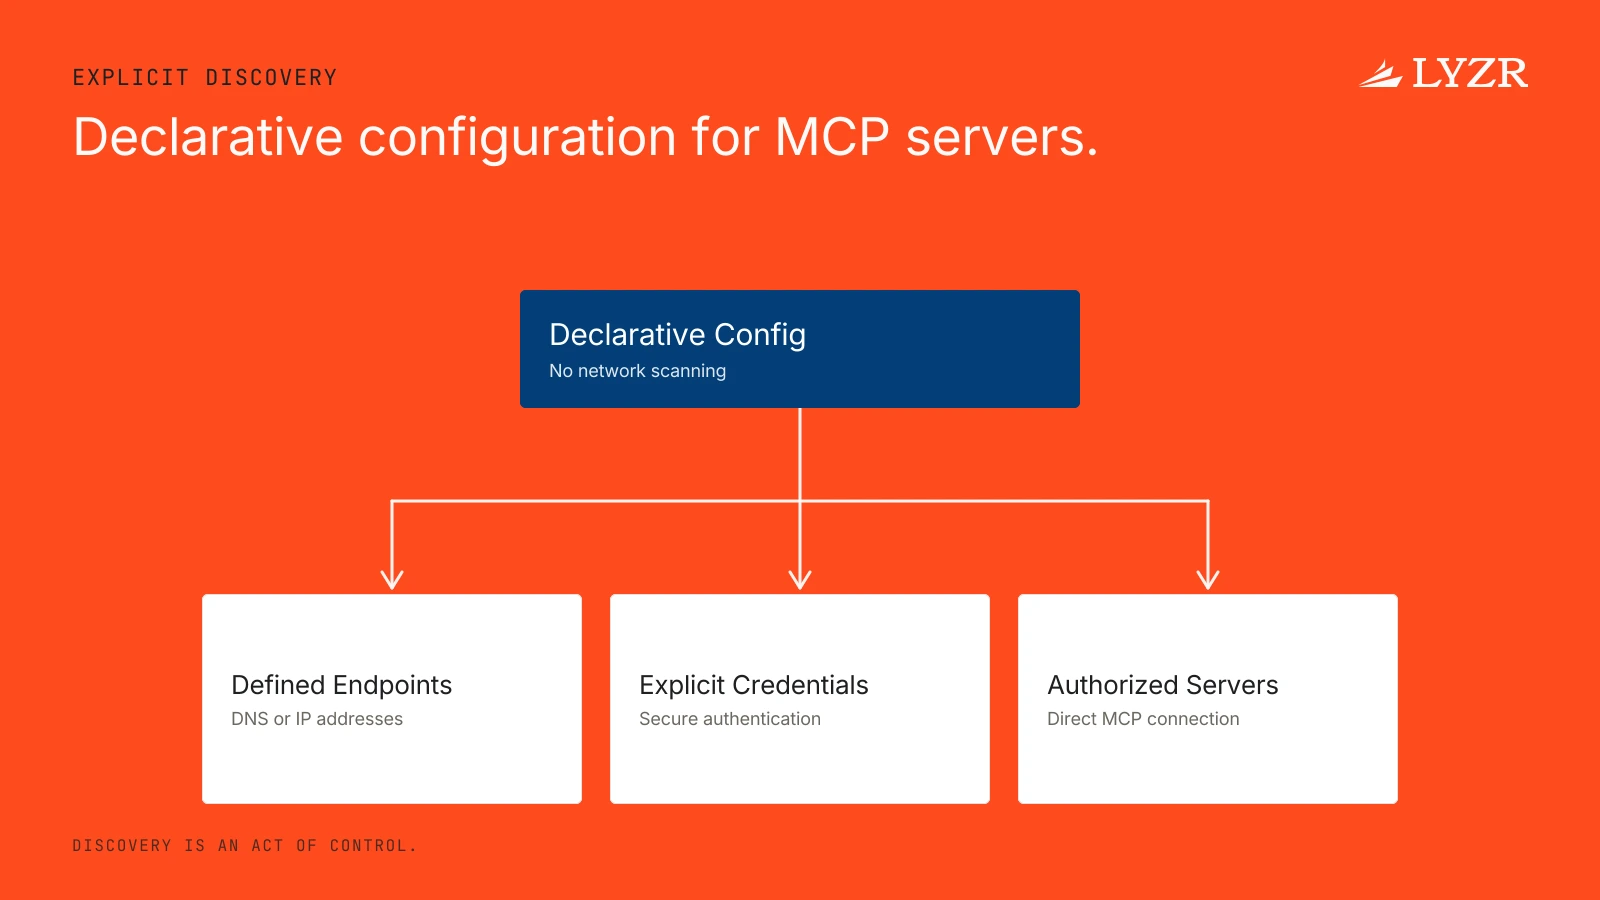
OpenController discovers MCP servers through explicit configuration, not automatic network scanning. You provide a list of server endpoints during setup, ensuring a secure and deterministic topology from the start.
This is a core design principle of OpenController by Lyzr, the governance layer for production AI agents.
A control plane is the neutral layer that governs everything beneath it. For AI agents, OpenController is that layer, and its authority begins with knowing exactly which components it is responsible for.
Explicit Discovery by Design
OpenController relies on a declarative approach.
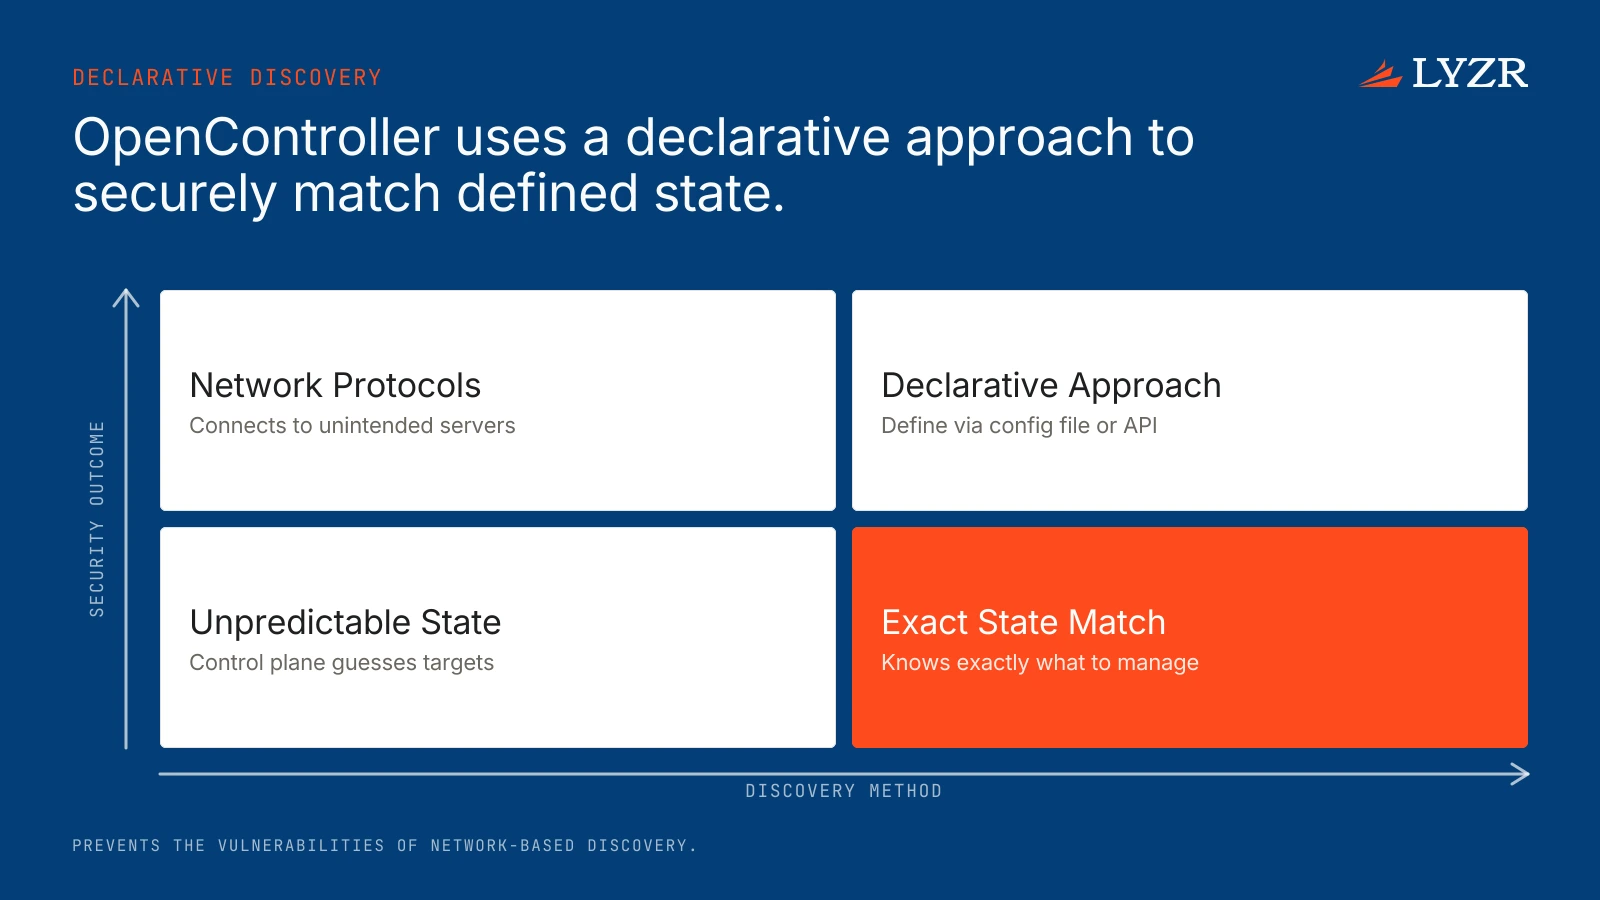
You define your infrastructure in a configuration file or through an API.
The control plane then works to match that defined state.
This isn't a limitation. It's a security feature.
It prevents the vulnerabilities and unpredictability of network-based discovery protocols, where a system might automatically connect to an unintended or insecure server.
In a production environment, you don't want your control plane guessing what it should manage.
You want it to know.
The Configuration Flow
The process is straightforward and designed to integrate with infrastructure-as-code (IaC) and GitOps workflows.
-
Define Endpoints. You specify the network addresses, like DNS names or IP addresses, of your MCP servers in the OpenController configuration.
-
Provide Credentials. Alongside each endpoint, you supply the necessary authentication credentials or tokens for OpenController to establish a secure, trusted connection.
-
Initiate Connection. OpenController uses this information to connect directly to the specified servers. It does not scan or probe the network for other potential targets.
-
Register and Monitor. Upon a successful, authenticated connection, the MCP server is registered within the control plane. It appears in your dashboard and becomes available for agent orchestration, governance policies, and observability.
Why We Avoid Automatic Discovery
Automatic discovery can create more problems than it solves in complex enterprise environments.
Network scans are noisy. They often trigger intrusion detection systems and are frequently blocked by firewalls in properly segmented networks.
The risk of mis-identification is also significant. A development server could be accidentally pulled into a production governance scope, or a rogue instance could be connected.
Explicit configuration ensures that AI agent governance is managed by deliberate policy, not by chance.
It guarantees that OpenController only connects to and manages the exact servers you have authorized, providing a clear and auditable infrastructure map.
The Takeaway: Discovery is an Act of Control
OpenController’s server discovery method is a deliberate choice.
It is a configuration-driven process built for the security, predictability, and auditability that production AI systems demand.
You tell the control plane what to manage. It never assumes.
If you have questions about how OpenController fits into your specific infrastructure, let's talk.
Want to see how it fits your stack? Talk to us about OpenController by Lyzr.
Got a use case in mind?
8 weeks from use case to agents running in production.
Platform, people and FDEs, all in. Bring your environment. We'll co-build and stay until it's live.
Talk to UsFree resource
101 AI Agents Use Cases
100+ production-ready AI agent use cases across Marketing, Sales, HR, Banking, Insurance, Operations and a lot more
Download now