Keeping agents compliant while they touch patient data is mostly a question of control, not of model choice.
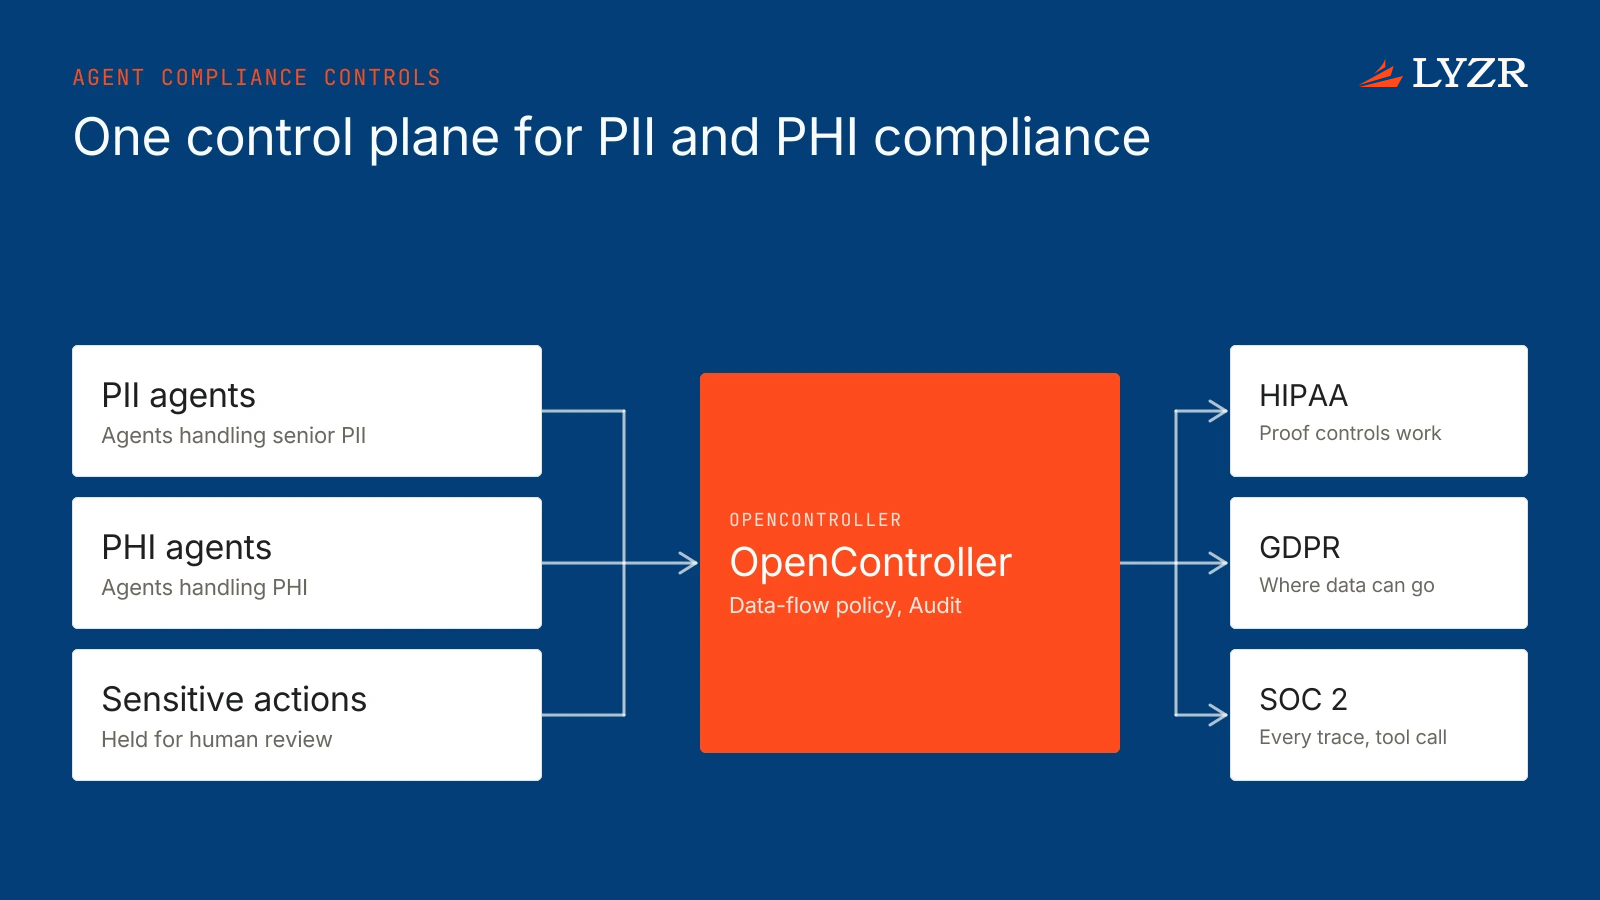
Lyzr's control plane supports HIPAA, GDPR, and SOC 2 by giving you the tools to enforce data handling policies, trace every agent action, and prove your controls to auditors.
It does this with OpenController by Lyzr, the control plane for enterprise AI agents.
Every production agent stack needs a control plane. OpenController is a framework-agnostic, cloud-agnostic one, built for enterprise governance.
It closes the gap between a working prototype and a production-safe agent that can handle sensitive data like PII and PHI.
How OpenController Controls Data Flow
Compliance starts with dictating where data can and cannot go.
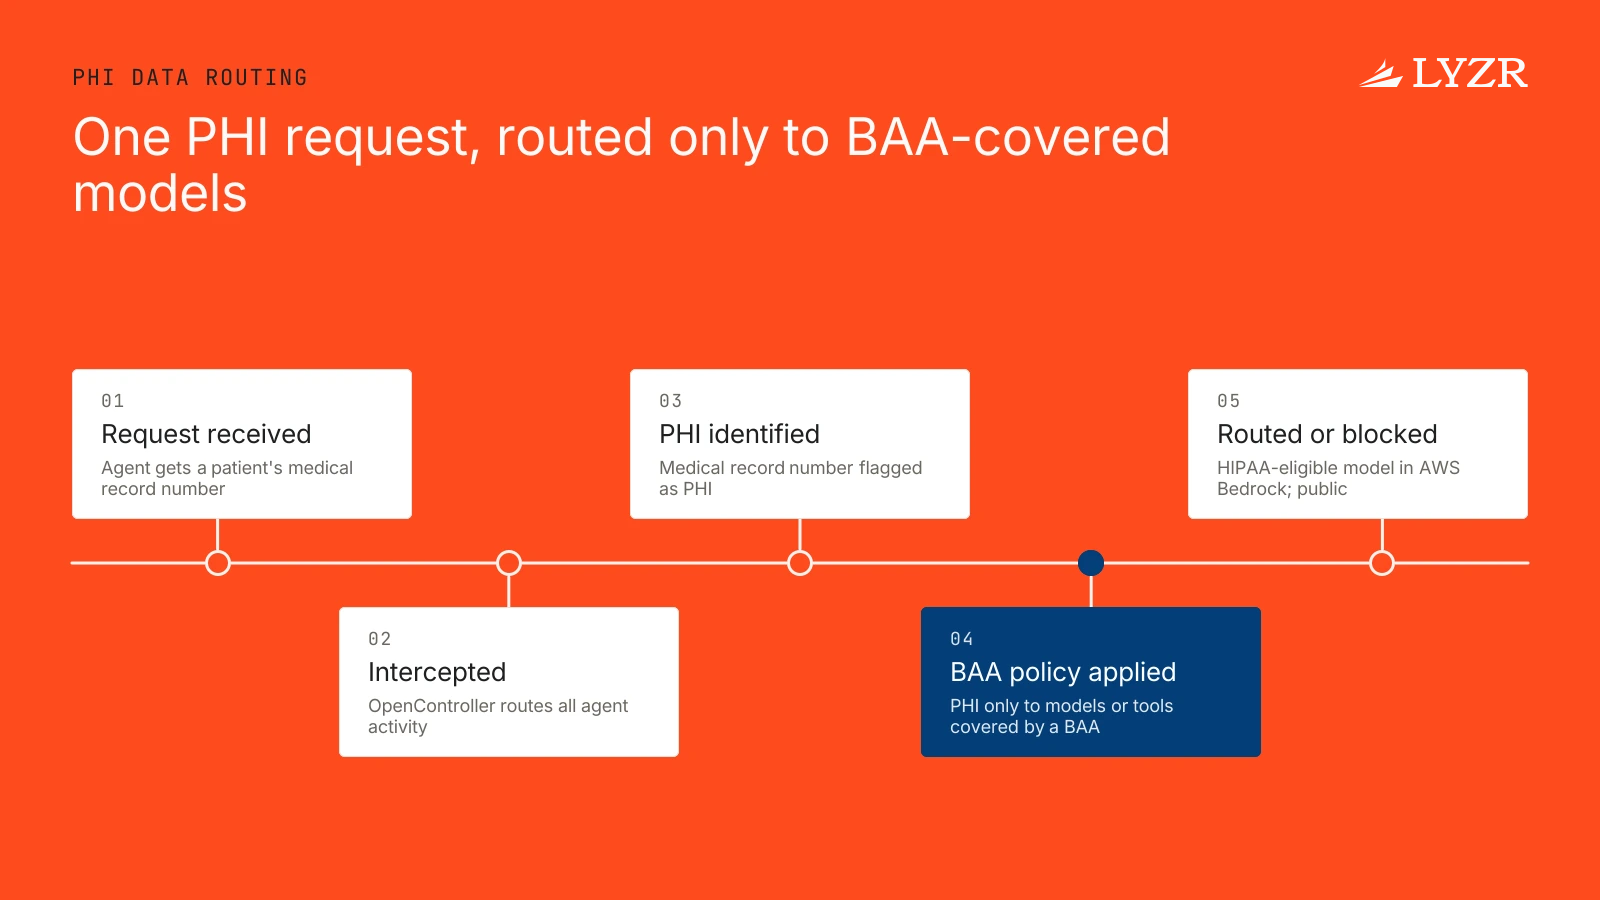
OpenController acts as a central router for all agent activity. You define the policies.
It enforces them.
For example, a policy can state that any data identified as PHI must only be processed by models or tools covered by a Business Associate Agreement (BAA).
An agent might receive a request containing a patient's medical record number.
OpenController intercepts this. It identifies the PHI.
It then routes the request to a HIPAA-eligible model, like one running in AWS Bedrock, and blocks any attempt to send it to a general-purpose public API.
This same principle applies to data residency for GDPR. You can set rules to ensure EU citizen data is processed only within approved regions.
The control plane, not the agent's code, becomes the source of truth for data handling rules.
The Audit Trail That Satisfies Auditors
Meeting SOC 2 or HIPAA requirements isn't just about having controls.

It's about proving they are working, consistently.
OpenController by Lyzr generates the audit trail that compliance teams actually need. Its observability layer surfaces every trace, every tool call, every output.
When an agent interacts with a senior's data, OpenController records:
- The exact input received.
- Which user or system triggered the agent.
- The full chain of thought of the agent.
- Every tool it called, with the exact parameters.
- The raw LLM prompts and completions.
- The final output delivered.
This isn’t just a raw log file. It’s a structured, attributable record of every event.
For a SOC 2 audit, you can instantly pull the complete history for any transaction to demonstrate that your security and data handling controls were enforced.
You can prove why a decision was made and confirm that no unauthorized actions were taken.
Why Human Approval Gates Are Essential
For the most sensitive operations, full automation carries too much risk.
Especially with PII and PHI.
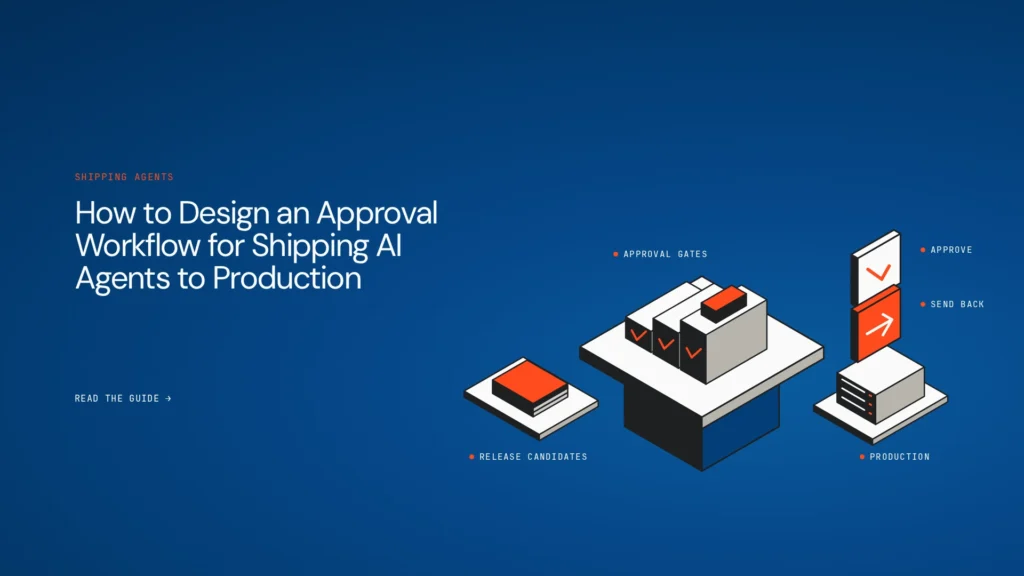
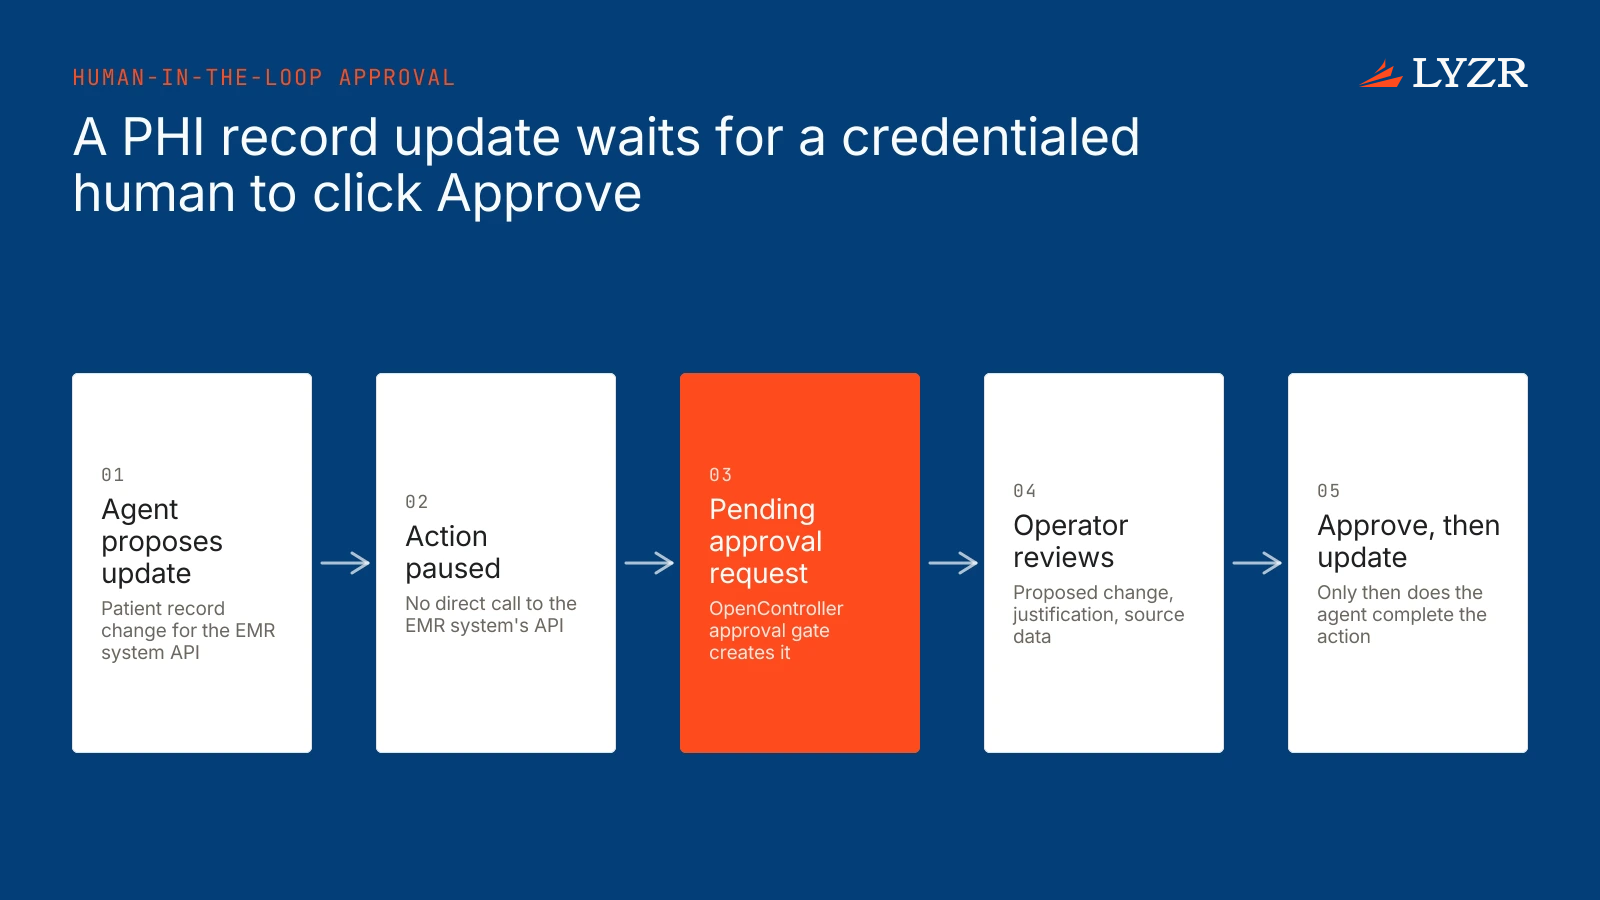
OpenController's approval gates enforce human-in-the-loop review before any consequential agent action.
An agent might determine that a patient's record needs to be updated. Instead of directly calling the EMR system's API, the agent's proposed action is paused.
OpenController creates a pending approval request.
A credentialed human operator receives a notification. They review the proposed change, its justification, and the source data in a simple interface.
Only after they click "Approve" does OpenController allow the agent to complete the action.
This creates a powerful, auditable control. You get the efficiency of the agent identifying the work to be done, with the safety of human judgment at the critical moment.
The Takeaway
Compliance for AI agents doesn't come from the model. It comes from the infrastructure that governs them.
You need a control plane to enforce policy, trace every action, and mandate human oversight for sensitive tasks. That is how you put agents to work on PII and PHI safely.
If you need to prove compliance for your AI agents, let's talk.
Want to see how it fits your stack? Talk to us about OpenController by Lyzr.
Got a use case in mind?
8 weeks from use case to agents running in production.
Platform, people and FDEs, all in. Bring your environment. We'll co-build and stay until it's live.
Talk to UsFree resource
101 AI Agents Use Cases
100+ production-ready AI agent use cases across Marketing, Sales, HR, Banking, Insurance, Operations and a lot more
Download now