An autonomous agent making an unapproved API call is a security incident waiting to happen.
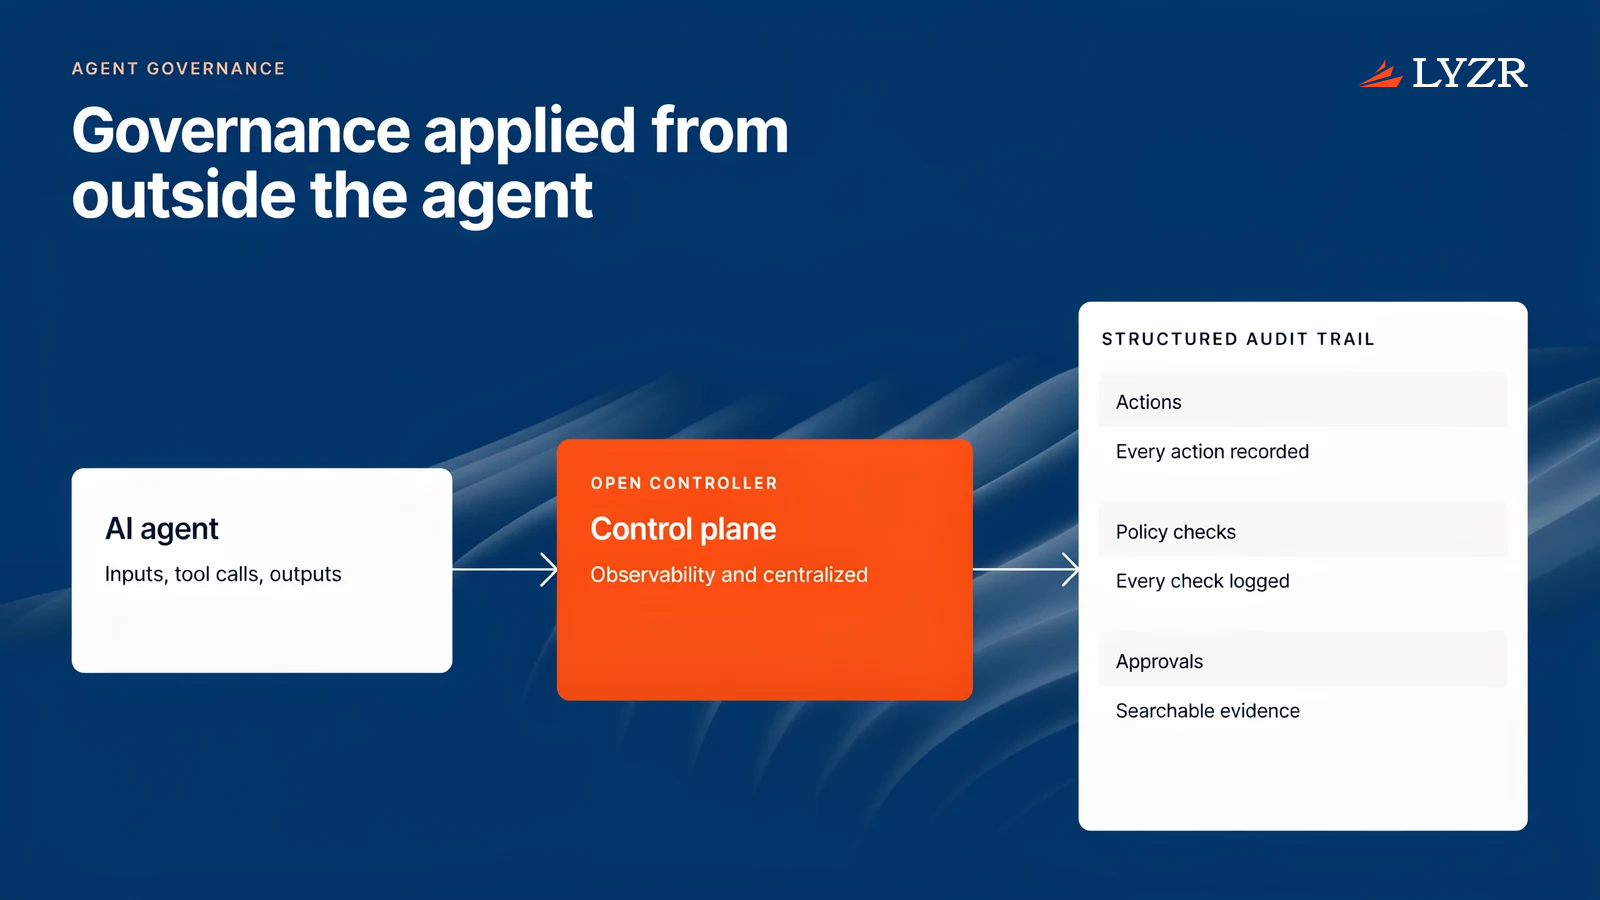
Governance in Lyzr's control plane is managed by separating policy from the agent's logic. It is enforced through observability, approval gates, and a complete audit trail.
This is the core function of OpenController by Lyzr, the governance layer for production AI agents.
A control plane is the neutral layer that governs everything beneath it. For AI agents, OpenController is that layer.
It closes the gap between a working prototype and a production-safe agent.
How Governance Is Enforced
Agent governance isn't a feature you bolt on. It’s a set of controls applied from outside the agent itself.
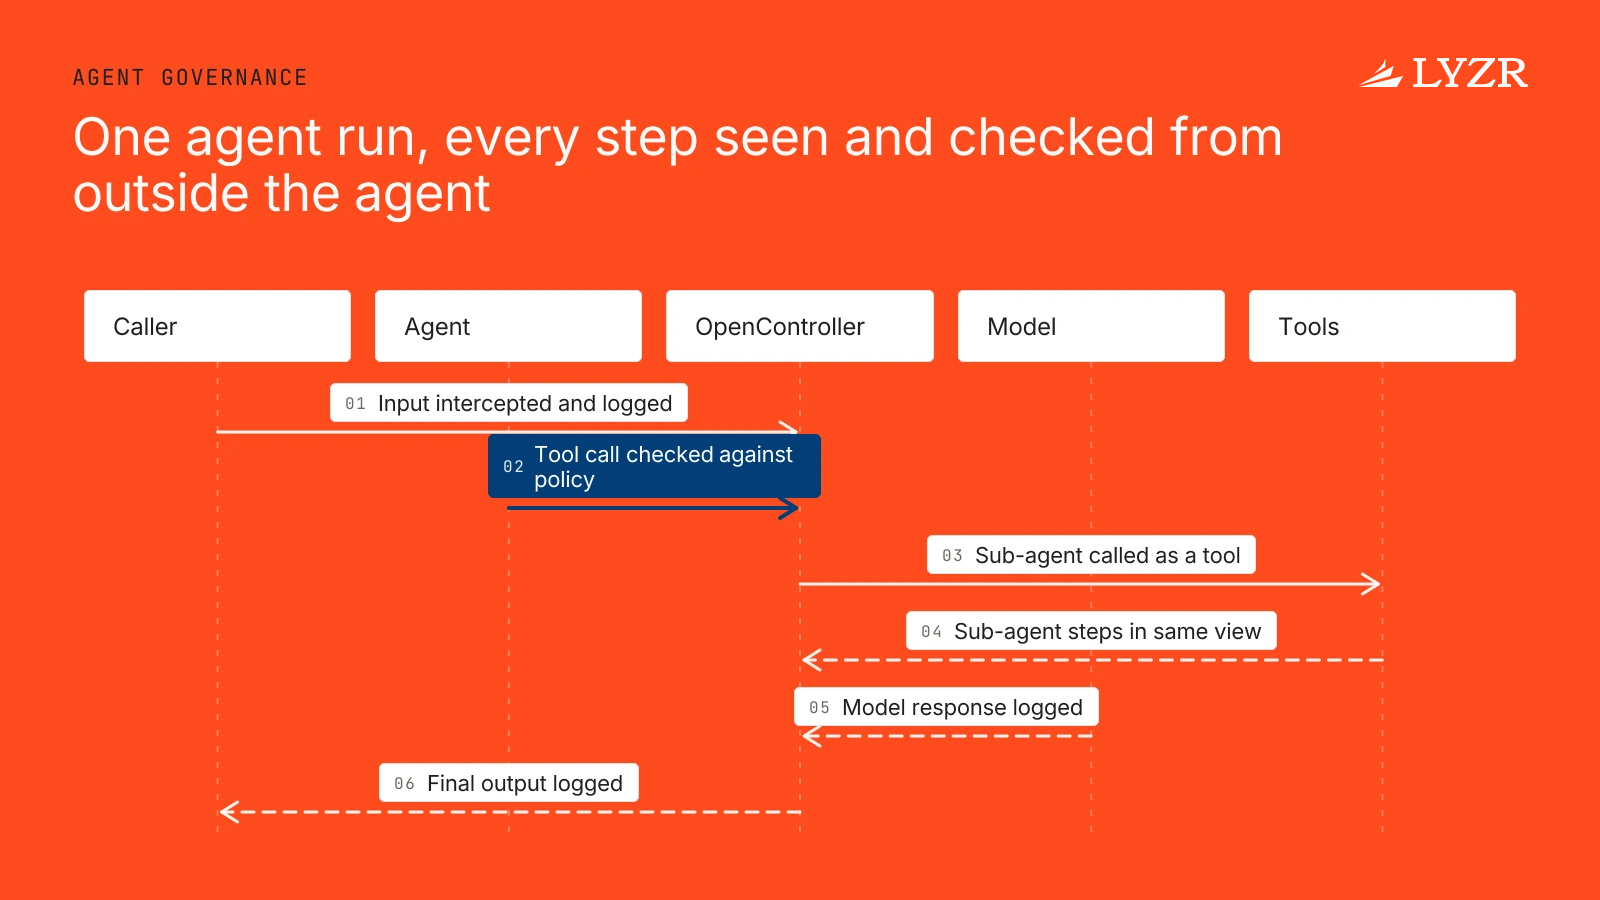
OpenController enforces governance through three primary mechanisms.
1. Complete Observability
You cannot govern what you cannot see.
OpenController intercepts and logs every input, every tool call, every model response, and every final output.
This creates a single, unified view of agent activity, even when an agent calls multiple sub-agents as tools.
Full visibility is the foundation of control.
2. Centralized Policy Management
Policies live in the control plane, not in the agent's code.
You define rules about which tools an agent can use, what data it can access, and which actions require oversight.
For example, you can create a policy that blocks any agent from calling a "delete_user" API endpoint directly.
This decouples your safety rules from your agent's development lifecycle.
3. Human-in-the-Loop Approval Gates
For consequential actions, autonomy is a liability.
OpenController’s approval gates pause an agent’s execution before it performs a critical task, like sending a customer communication or modifying a database record.
A designated human must review the proposed action and its context, then explicitly approve or deny it.
This provides a manual check on automated processes, ensuring a human is accountable for high-stakes decisions. The entire interaction is logged for the audit trail.
The Audit Trail for Compliance
Every action, policy check, and approval is recorded.
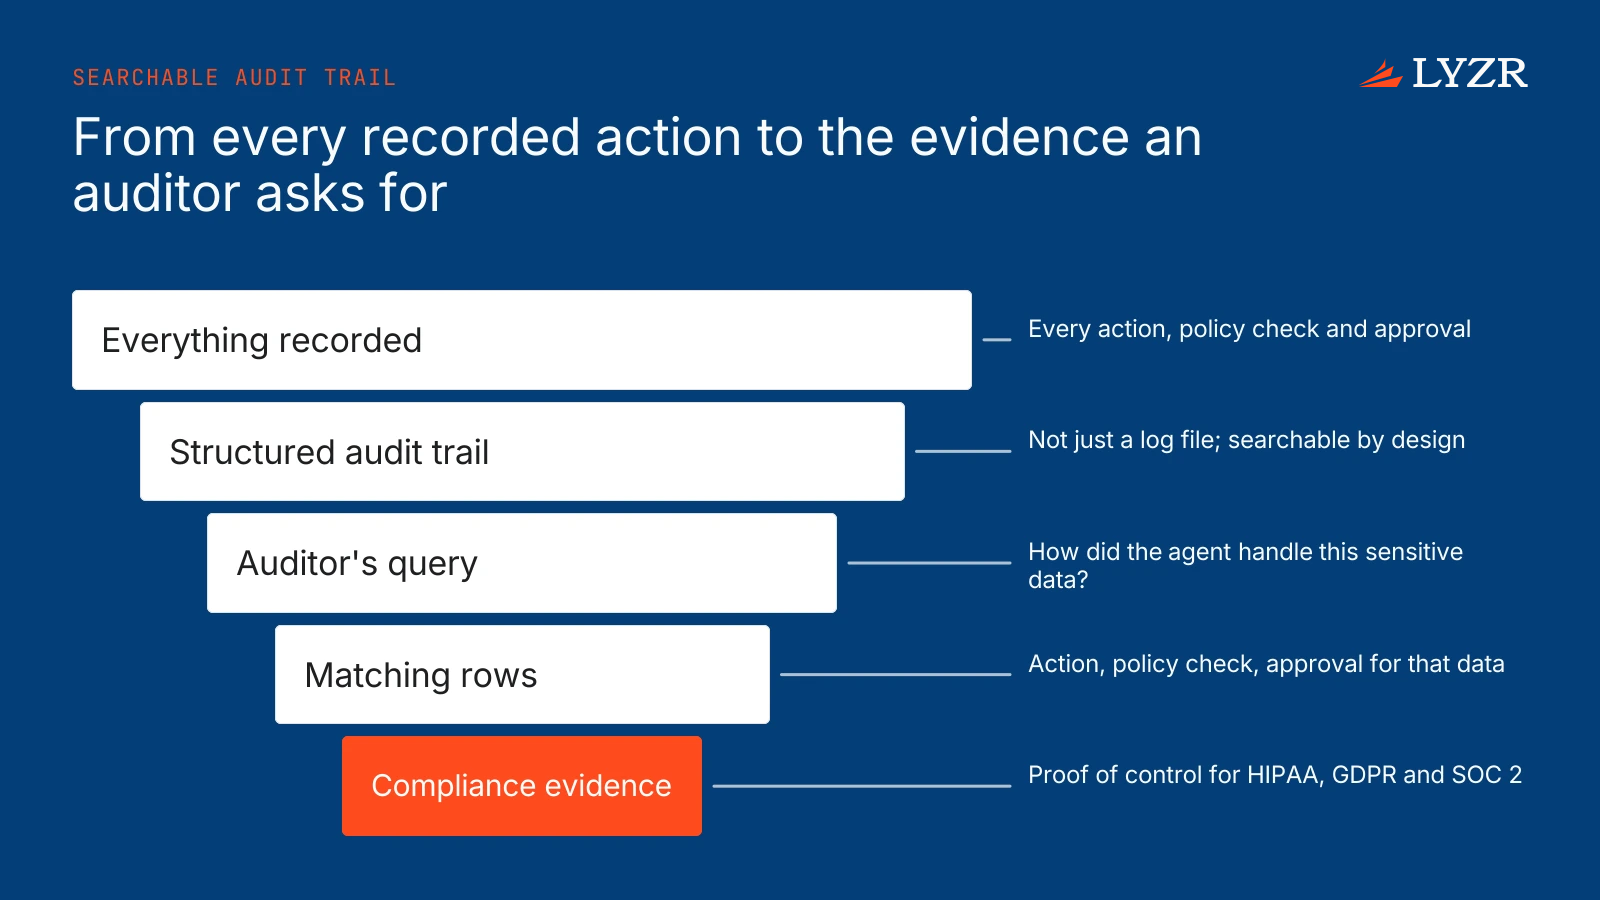
This isn't just a log file. It's a structured, searchable audit trail built for security and compliance teams.
When an auditor asks you to prove how an agent handled a specific piece of sensitive data, OpenController provides the evidence.
This is how you demonstrate control and meet requirements for frameworks like HIPAA, GDPR, and SOC 2.
Frequently asked questions
Does this work with agents I've already built?
Yes. OpenController accepts agents built on any framework, including LangChain, CrewAI, LangGraph, or a raw SDK.
Nothing needs to be rebuilt to be governed.
Is governance tied to a specific LLM?
No. OpenController is model-agnostic. It governs the agent's actions regardless of which LLM they run on, whether it's from OpenAI, Anthropic, Google, or a self-hosted model.
Your Governance Layer for Production AI
Effective governance isn't about restricting agent capabilities. It's about enabling them to operate safely in production.
By treating governance as an infrastructure problem solved by a control plane, you get the control you need without slowing developers down.
If you're ready to enforce policy on your AI agents, talk to a Lyzr specialist.
Want to see how it fits your stack? Talk to us about OpenController by Lyzr.
Got a use case in mind?
8 weeks from use case to agents running in production.
Platform, people and FDEs, all in. Bring your environment. We'll co-build and stay until it's live.
Talk to UsFree resource
101 AI Agents Use Cases
100+ production-ready AI agent use cases across Marketing, Sales, HR, Banking, Insurance, Operations and a lot more
Download now