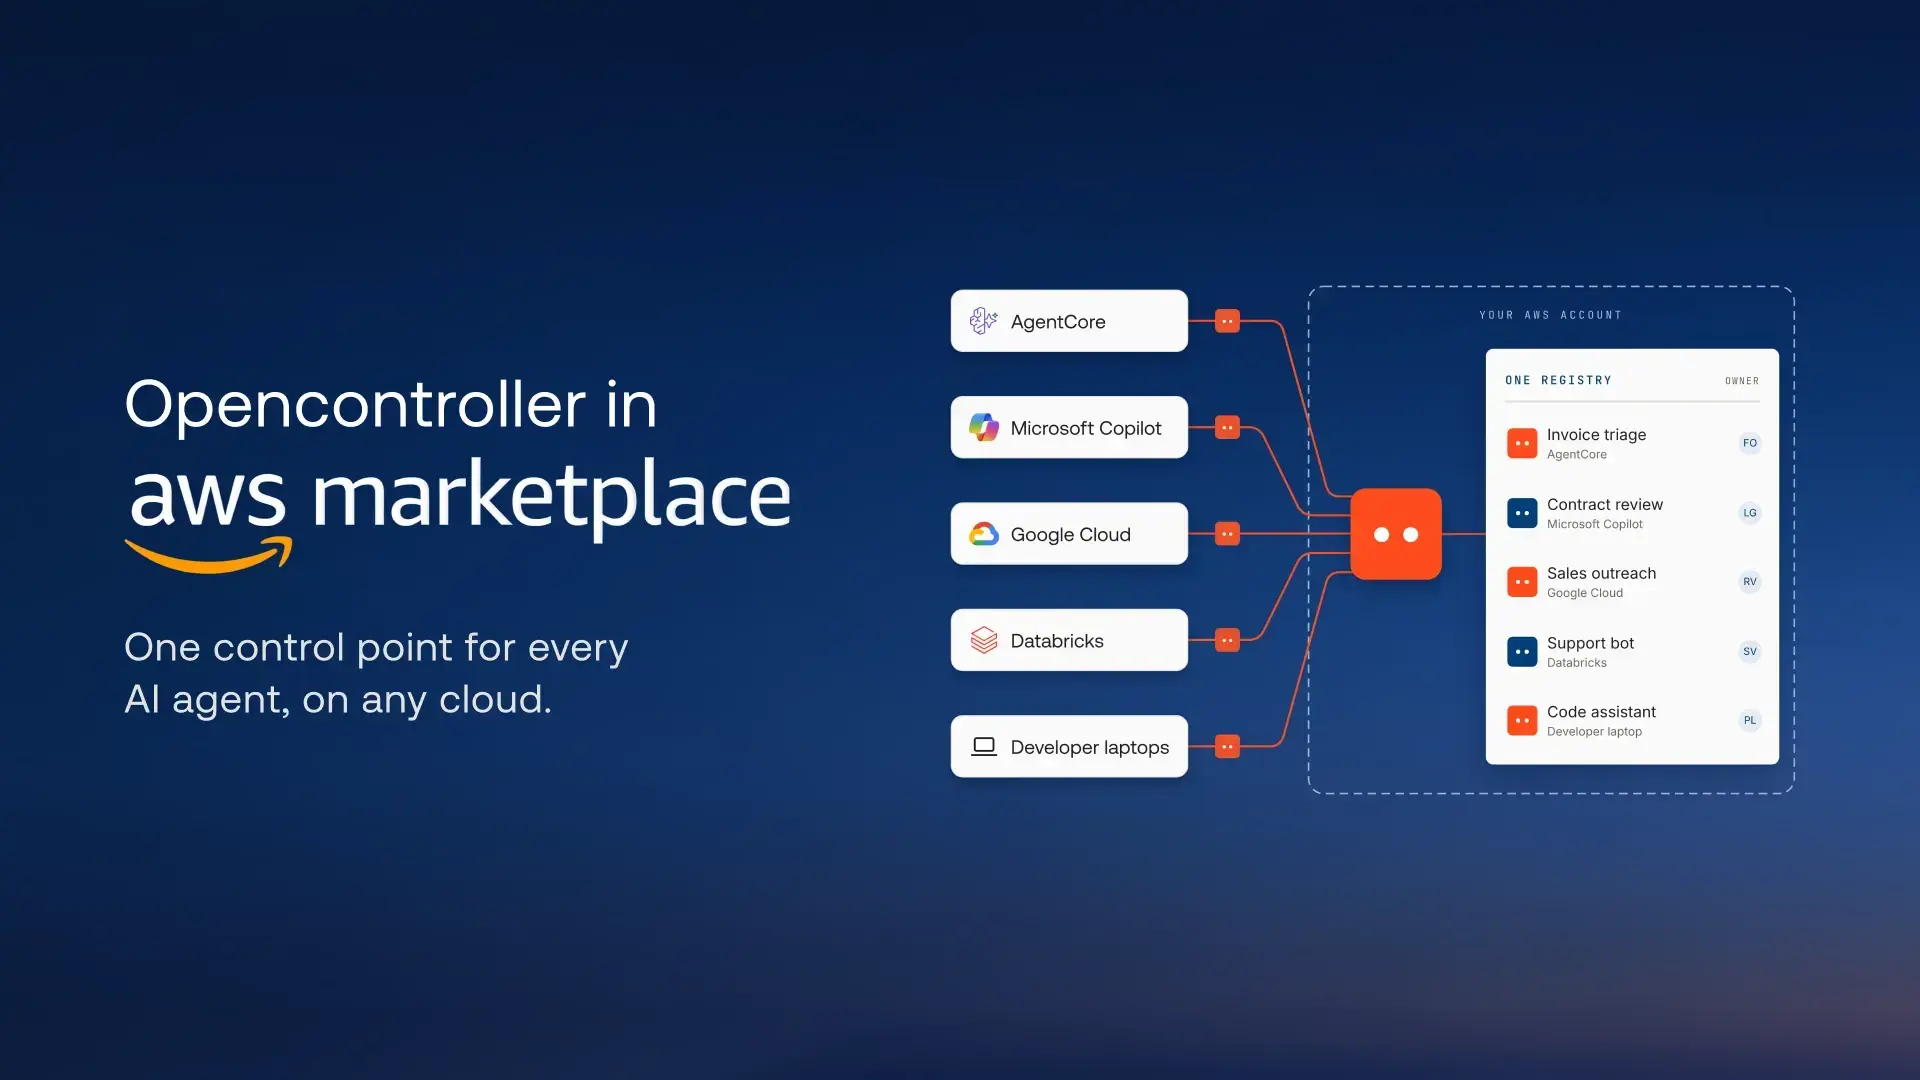
Opencontroller is now on AWS Marketplace, and it runs inside your own AWS account.
Ask your CIO how many AI agents the company runs. Then ask who owns each one, and who can switch one off.
Most of the time you’ll get a spreadsheet. Sometimes you’ll get a pause.
Why nobody has the full list
One team builds an agent in Copilot Studio. Another ships one on Amazon Bedrock AgentCore. A developer runs a coding agent on a laptop. Every platform has its own console, its own keys and its own bill, so nobody ever sees the whole picture in one place. And builders move teams, and sometimes companies, long before anyone asks who owns what they built.
The cost is already showing up. IBM’s 2025 Cost of a Data Breach Report found that one in five organizations had a breach tied to shadow AI. Of the organizations whose AI models or apps were breached, 97% had no access controls on them.
That’s the gap Opencontroller was built for. As of today it’s on AWS Marketplace.
What it does about it
It starts by looking. A read-only scan of your clouds, clusters and developer laptops builds a live inventory of every agent, plus the models, tools, MCP servers, identities and keys each one uses. It never runs an agent, reads a conversation or pulls a secret. This is how you find the agents nobody told IT about.
Then it makes ownership real. Every agent gets a named owner, an approval and its own identity before it reaches production, which means the shared API key can finally be retired. Model calls go through a gateway that holds them to a budget and blocks personal data, secrets and prompt injection before the call lands. And when an agent goes wrong, its owner can shut it down on the platform it runs on, from one console, with a name and a reason logged against the change.
It runs in your account
A tool that sees every agent, every key and every prompt has to live somewhere you trust. So Opencontroller runs on Amazon EKS inside your own AWS account, under your own KMS keys. Prompts, keys and telemetry don’t need to leave it. If the first thing your security team asks about any governance tool is where the data goes, this is the answer we built around. It can also run on-premises, hybrid or fully air-gapped.
If you build on AgentCore
Nothing changes there. Opencontroller reads AgentCore with a read-only IAM role and checks it against the Security Hub controls for AgentCore. Then it applies the same registry, budgets and policies to the agents you run on Microsoft, Google Cloud and Databricks. You keep AgentCore. You add a single view of everything outside it.
Who’s already using it
Our customers run it across three clouds: one registry, five controls on every deployment, and nobody had to move off their tools. Some of our named customers are Prophet, Verifone, Nordstrom, Accenture, WTW, KPMG and many others. If something goes wrong in a deployment, it rolls back in one click.
How to buy it
The way you already buy AWS. Ask your AWS account team, or email AWS-Marketplace@lyzr.ai, for a private offer. It lands on your AWS invoice and can count toward your AWS commitment; check your agreement for the exact terms. A first environment is up in under a week.
Come find us at re:Invent
We’re at AWS re:Invent, booth #134, November 30 to December 4. Bring the agent you worry about most, and we’ll scan it with you while you watch. Book 20 minutes.
CTA button: See Opencontroller on AWS Marketplace → https://aws.amazon.com/marketplace/pp/prodview-f42iviajz4fsm
Secondary links: case study, recorded demo, lyzr.ai/aws-reinvent.
Book A Demo: Click Here
Join our Slack: Click Here
Link to our GitHub: Click Here
Got a use case in mind?
8 weeks from use case to agents running in production.
Platform, people and FDEs, all in. Bring your environment. We'll co-build and stay until it's live.
Talk to UsFree resource
101 AI Agents Use Cases
100+ production-ready AI agent use cases across Marketing, Sales, HR, Banking, Insurance, Operations and a lot more
Download now