The best platform for AI data privacy compliance in a bank depends on the job: finding sensitive data, stopping it leaking into AI tools, governing the AI itself, or proving to an examiner that the controls exist and who approved them. This guide compares nine platforms across those jobs. Madison, Lyzr’s agentic GRC product for US banks and credit unions, is the pick for the proof job: it links privacy and security rules to obligations, policies, controls, tests and evidence, with a named person signing. Opencontroller by Lyzr covers per-call policy for agents. Nightfall controls data movement, BigID finds and classifies data, Mitratech Alyne, IBM watsonx.governance and ServiceNow govern AI, Behavox surveils communications, and Perfios and PrivaTrust serve India’s DPDP Act. Madison does not scan data or redact prompts, so most banks pair it with a data tool.
TL;DR
- Four jobs, not one: find the data, control where it goes, govern the AI, prove it to a supervisor. No platform here does all four.
- Best for the proof job: Madison (our product) holds the rule-to-evidence record. Read its limits: it does not scan data or redact.
- Best for data leaving through AI: Nightfall describes inline control across agents, MCP servers, SaaS and email. BigID describes access control and redaction inside AI prompts and responses.
- Best for AI governance workflows: Mitratech Alyne, IBM watsonx.governance and ServiceNow. Their own pages differ on what they enforce at runtime.
- Not every name belongs: Behavox is communications surveillance, not a privacy tool, and the DPDP suites target India. We could not verify Cytrusst or Privacy Global at all.
- How we judged: vendor pages and press, with gaps stated. “Not described” means we did not find it, not that it is absent.
What does AI data privacy compliance need to cover in a bank?
AI data privacy compliance means customer and employee data that enters, moves through or comes out of AI systems is handled the way the bank’s privacy and security obligations require, and the bank can show it. That covers training and prompt data, agents reading records, vendors that process data, and the evidence trail. If you are choosing tools for the wider problem, our earlier guide to best tools for AI data privacy and compliance for banks compares a different set of vendors by job. This guide focuses on data movement, AI governance platforms and regional privacy suites.

| Privacy need | What good looks like | Where it usually comes from |
|---|---|---|
| Know where sensitive data is | Discovery and classification of PII, card and transaction data across cloud, SaaS and on-premises systems. | Data security and privacy platforms |
| Stop leaks into AI tools | Inline inspection of prompts, files, agent calls and MCP traffic, with block or redact actions. | Data movement control, gateways |
| Limit what agents can reach | Per-agent permissions, per-tool authorization and credentials the agent never holds. | Control plane or gateway |
| Know which AI exists | An inventory of models, agents and vendors, including ones nobody registered. | AI governance and discovery tools |
| Map rules to controls | Each privacy or security obligation tied to a policy, a control and a test. | GRC record |
| Show who approved what | Decisions signed by a named person against the exact version, ready for an examiner request. | GRC record |
How we assessed: we read each vendor’s own pages and press coverage, and say where a page was vendor-authored, an advertorial or unreachable. Nearly all sources are vendor material. “Not described” means not found on the pages we reviewed, not that the capability is absent. Madison and Opencontroller are our products and are listed first for that reason. This is not legal advice.
The best AI data privacy compliance platforms for banks at a glance
| # | Platform | Best for | Job | Watch for |
|---|---|---|---|---|
| 1 | Madison by Lyzr | The supervisor record: rule, policy, control, test and evidence, signed | Proof | Does not scan data, redact or block |
| 2 | Opencontroller by Lyzr | Per-call policy, egress control and signed audit trail for agents | Control | Not described as a data classifier |
| 3 | Nightfall AI | Controlling sensitive data moving to AI agents, MCP, SaaS and email | Control | No certifications named on pages read |
| 4 | BigID | Discovering and classifying data, and controlling it in AI prompts | Discover | Deployment and certifications not detailed |
| 5 | Mitratech Alyne | Cloud GRC: mapping regulations and evidence to controls | Govern | No privacy features or AI inventory on its product page |
| 6 | IBM watsonx.governance | AI model governance with guardrails and obligation mapping | Govern | Key page is dated 2024 |
| 7 | ServiceNow AI Control Tower | An AI asset inventory inside the ServiceNow platform | Govern | Runtime blocking confirmed only for MCP in docs |
| 8 | Behavox | Communications surveillance and archiving with ISO/IEC 42001 | Conduct | Not a data privacy tool |
| 9 | Perfios DPDP Suite, PrivaTrust | Consent and privacy operations under India’s DPDP Act | Discover, consent | India-first; limited US relevance |
Madison by Lyzr
Madison is a workforce of AI agents for compliance and risk in US banks and credit unions. It reads the rules, your policy and procedure library and your examination history, builds a live map of how they connect, and hands finished, sourced work to a named person who decides.
Every data tool below produces a log, a report or a policy setting. Someone still has to show which obligation it satisfies and who approved it. Madison holds the chain: regulation, rule section, obligation, applicability, policy, procedure, control, test, finding, remediation, evidence and request, as one connected record. A privacy or safeguards rule is read like any other rule and traced to the policy and control behind it. Vendors, models and agents are governed objects with owners and evidence, so a data tool’s report becomes evidence on the control it supports.

| Privacy compliance question | What Madison adds |
|---|---|
| Which AI vendors and agents touch our data? | Holds vendors, models and agents as governed objects with owners and evidence. See AI agent inventory for banks. |
| Which obligation does this control satisfy? | Traces the control back through policy and obligation to the rule text. |
| Do our policies cover the obligation? | Flags an obligation with no policy, a policy covering nothing, or an obligation with a policy but no control. |
| Who approved the control, and on which version? | Signs every decision against the exact version, with the signer’s role. |
| Can we answer the examiner? | Answers requests from the chain behind them, in one register. See how to map policies to controls with an agent. |

Best for: compliance, risk and audit teams at US banks and credit unions who need the record behind their AI data controls. See AI in compliance vs AI governance and what regulators ask banks about AI agents. Start with a Madison working session.
2. Opencontroller by Lyzr
Best for: controlling what agents can reach and send, with signed records of what they did.
Opencontroller is Lyzr’s agent control plane. Each agent gets an immutable ID and a named owner. A gateway enforces egress policy per agent and applies budgets that refuse calls once spent. Each tool call is authorized by policy that reads the call’s arguments, so a rule can depend on the destination or amount, and credentials are brokered so the agent never holds them. Approvals cover publish, modify, disable and retire, with the approver never the requester. A signed audit trail records lifecycle events, model calls and tool executions, and a reversible quarantine refuses an agent’s calls without a redeploy. It discovers agents across clouds, clusters and devices, including unsanctioned AI clients and MCP configurations, and it runs in the customer’s cloud account.
Where it fits
It limits where an agent’s data can go and records every call, which is the agent side of data privacy. See best platforms for AI agent safety in regulated industries.
What to check
A gateway governs traffic that passes through it, so egress policy and discovery are what make it the only path. The Capability Reference does not describe data classification or content redaction, so pair it with a data tool. Confirm current capabilities with Lyzr.
Pick it if: your concern is what agents can reach and send, with separated approvals and a stop switch.
3. Nightfall AI
Best for: controlling sensitive data moving into AI agents, MCP servers, SaaS, email and endpoints.
Nightfall’s homepage says it controls data movement across AI agents, MCP servers, endpoints and SaaS, and a September 16, 2026 blog adds email, browser AI tools and named copilots and chat apps. The homepage describes an MCP gateway that approves servers, blocks the rest by default and enforces policy on every tool call. The blog says that, depending on the integration and channel, it can block, coach, redact, delete, revoke, quarantine or encrypt. Deployment is SaaS integrations through APIs plus a single endpoint agent deployed through MDM. Customer stories are mostly fintechs, and the pages say it can support programs aligned with PCI DSS, GLBA and SOX.

Pick it if: your first privacy risk is data leaving through AI tools, MCP servers and SaaS.
Sources: Nightfall homepage, blog (September 16, 2026) and MCP security blog (July 6, 2026). Vendor-authored.
4. BigID
Best for: discovering and classifying sensitive data, and controlling access to it in AI conversations.
BigID’s financial services page describes discovering, classifying, securing, governing and minimizing sensitive data across banking, payments, cloud, SaaS, analytics and AI environments, covering PII, card, KYC, IBAN, SSN and transaction data. A press release dated October 2, 2025 introduces access control for sensitive data in AI conversations, and the product page describes masking or redacting data in prompts and responses and showing which AI systems and identities can reach sensitive data. The page names PCI DSS, GLBA, NYDFS and SOX as requirements it helps support. We also covered BigID in our data privacy tools guide.

Pick it if: you need a data map and classification before setting rules for AI.
Sources: BigID financial services page (modified October 21, 2026), AI prompt security page and press release (October 2, 2025). Vendor-authored.
5. Mitratech Alyne
Best for: a cloud GRC platform that maps regulations and evidence to controls.
Alyne’s product page describes cloud risk assessment, policy and document mapping, and AI that maps regulations, frameworks and evidence to controls with human approval. Frameworks named include ISO 27001, SOC 2, SR 11-7, SOX and DFAST. A Mitratech blog dated October 16, 2026 calls Alyne, ServiceNow AI Control Tower and IBM watsonx.governance the strongest AI governance tools for financial services and lists Alyne first. It says AI inventory comes from Mitratech’s ClusterSeven discovery, not from Alyne alone.

Pick it if: you want a broad GRC platform and will add data and AI tools around it.
Sources: Mitratech Alyne product page (modified November 10, 2026) and Mitratech blog (October 16, 2026). Vendor-authored.
6. IBM watsonx.governance
Best for: AI model governance with risk assessment, guardrails and obligation mapping.
IBM’s December 11, 2024 announcement of version 2.1 describes discovering shadow AI deployments through Guardium AI Security, risk assessment and approval workflows, and real-time guardrails that detect PII, hate speech and faithfulness issues in prompts and outputs against set thresholds. A separate IBM blog describes using LLMs to map legal and regulatory requirements to controls, with components deployable on any cloud and on premises, and a BizTech article from December 5, 2025, built on IBM sources, covers model tracking and monitoring for banks.

Pick it if: you want model governance inside an IBM estate and will verify what is current.
Sources: IBM announcement (December 11, 2024), IBM obligations-to-controls blog and BizTech Magazine (December 5, 2025). Vendor-authored or vendor-sourced.
7. ServiceNow AI Control Tower
Best for: an AI asset inventory and lifecycle workflow inside the ServiceNow platform.
ServiceNow’s product page is now titled Super Intelligence Control Tower, while its documentation, updated October 28, 2026, still says AI Control Tower. The documentation describes an inventory of AI systems, models, prompts, datasets and MCP servers fed by discovery from external platforms and the instance, with governance posture, evaluation scores and lifecycle reviews. The product page names the EU AI Act, NIST AI RMF and the California AI Transparency Act and claims runtime governance.

Pick it if: ServiceNow is your system of record for IT and you want AI assets in it.
Sources: ServiceNow product page (undated) and documentation (updated October 28, 2026). Vendor-authored.
8. Behavox
Best for: communications surveillance and archiving, an adjacent control rather than a privacy tool.
Behavox describes AI-native compliance and conduct surveillance, with Quantum for voice and text across more than 50 languages, plus archive, trade surveillance and regulatory change products. A November 25, 2025 press release says Prescient Security, an independent third party, validated its AI management system against ISO/IEC 42001:2023, and lists SR 11-7 under alignment with global laws and standards. Its AI page says models are governed to SR 26-2, which it says supersedes SR 11-7.

Pick it if: you need communications surveillance and want a vendor with an ISO/IEC 42001 certificate.
Sources: Behavox press release (November 25, 2025), homepage and AI page. Vendor-authored.
9. Perfios DPDP Suite and PrivaTrust by eMudhra
Best for: banks with India operations that must meet the Digital Personal Data Protection Act.
Perfios launched its DPDP Suite on March 30, 2026 in a syndicated press release, describing data discovery and classification, automated records of processing, consent governance with verifiable records, data principal rights, cookie consent and database activity monitoring, India-first and in 22 scheduled languages. PrivaTrust by eMudhra describes consent management, discovery, request handling, a remediation hub for masking, encryption, deletion and access restriction, on-premises deployment with air-gapped feature parity and more than 15 regulations including DPDP, GDPR and CCPA. Its banking pages are India-specific, citing RBI data localization.

Pick it if: you operate in India or run a global privacy program.
Sources: Tribune India (Perfios release, March 30, 2026) and eMudhra PrivaTrust pages. Vendor-authored.
Where does data leak into AI, and which platform covers each point?
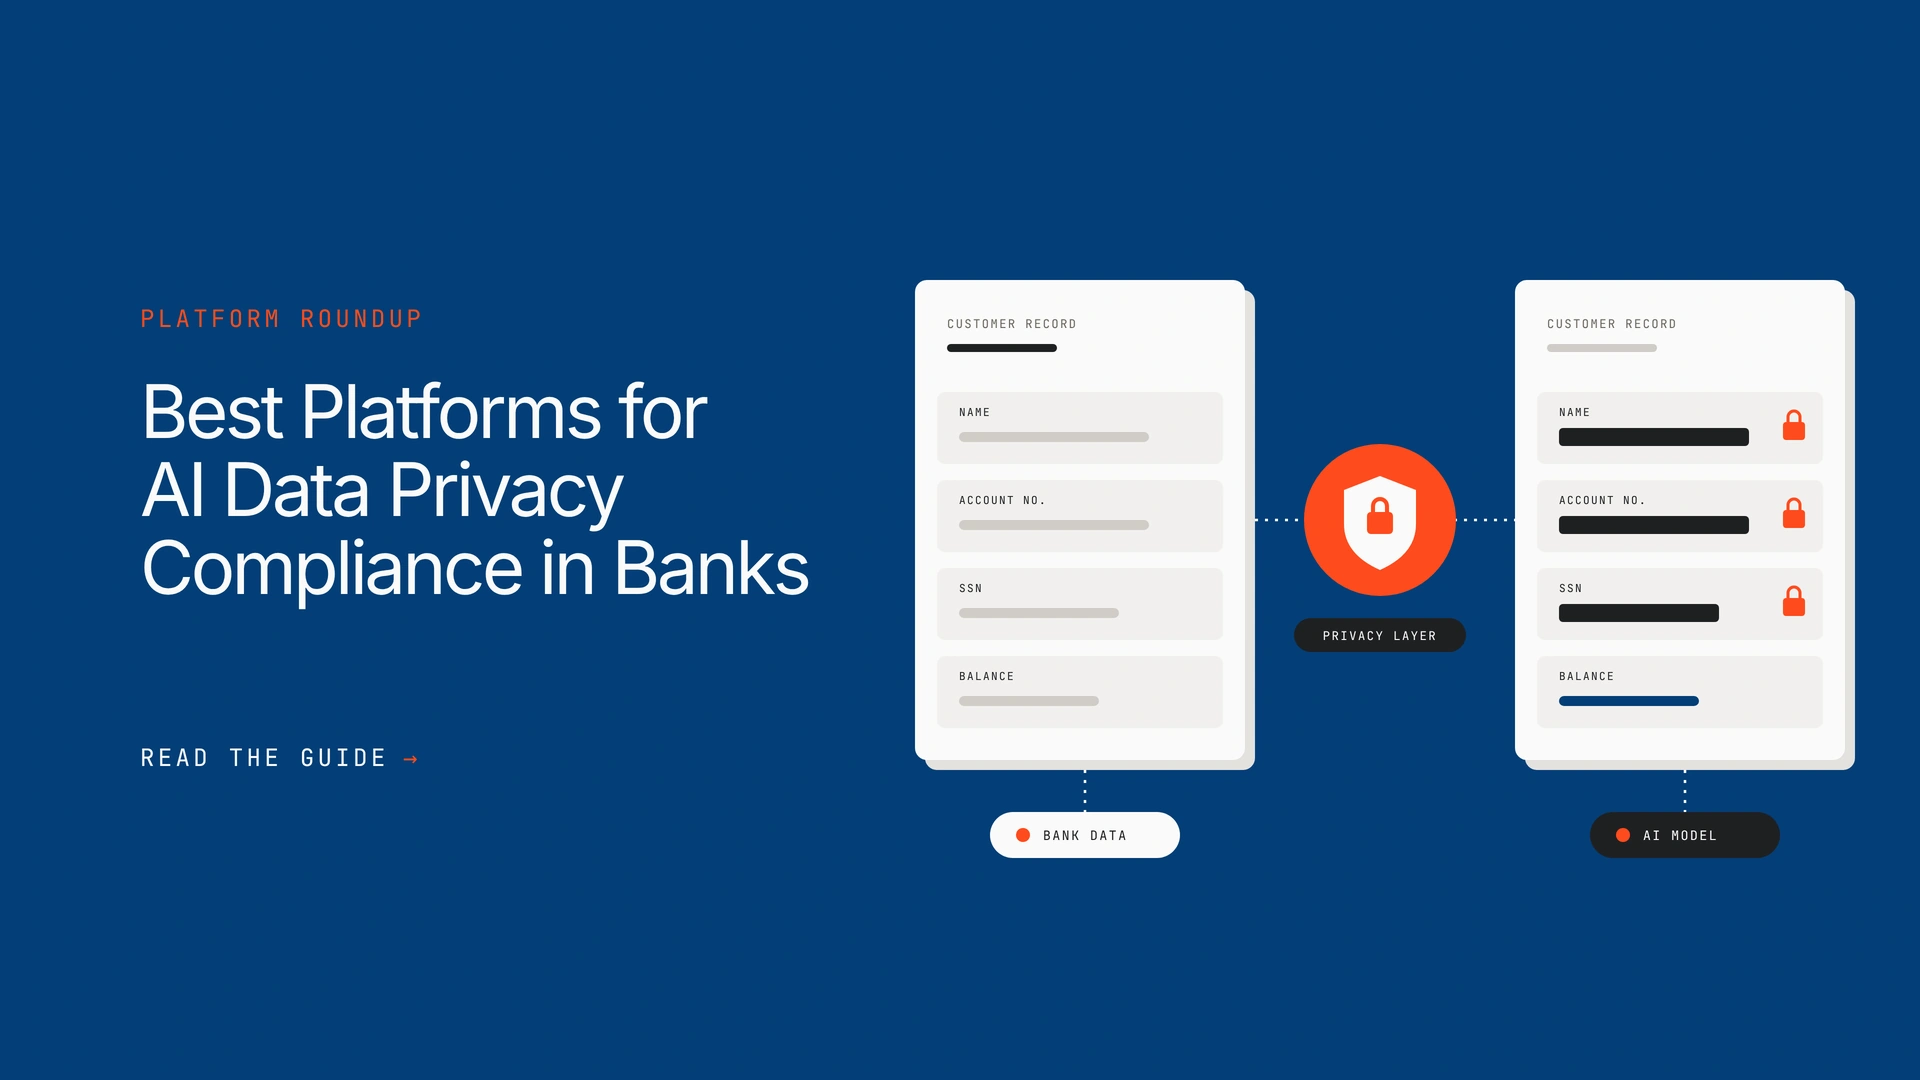
Sensitive data reaches AI along four routes: it sits in systems an agent can read, it is pasted or sent into an outside tool, it is processed by a vendor’s model, and it ends up in logs and archives. Each route needs a different control, which is why banks combine tools. See voice AI guardrails for the same pattern in contact centers.

How do the AI data privacy platforms compare?
| Platform | Finds and classifies data | Controls data going to AI | Redacts or blocks | AI inventory | Regulatory mapping | Evidence with named approver | Banking content |
|---|---|---|---|---|---|---|---|
| Madison | No | No | No | Registers vendors, models, agents | Yes: rule to obligation to control | Yes: signed decisions | US banks and credit unions |
| Opencontroller | Not described | Egress policy, per-tool authorization | Refuses calls; brokers credentials | Discovery incl. unsanctioned clients | No | Signed audit trail | Not bank-specific |
| Nightfall | Detects in motion | Yes: agents, MCP, SaaS, email | Block, redact, others by channel | Shadow AI controls | Supports PCI DSS, GLBA, SOX programs | Not described | Fintech customers |
| BigID | Yes: core | Access control in prompts | Mask or redact | AI systems and identities with access | PCI DSS, GLBA, NYDFS, SOX support | Not described | Financial services page |
| Alyne | Not described | No | No | Via ClusterSeven (blog) | Yes: frameworks to controls | Evidence, human approval | SR 11-7, SOX named |
| watsonx.governance | Not described | PII guardrails | Detects against thresholds | Guardium AI Security | Obligations to controls | Assessments, approvals | IBM blog on banks |
| ServiceNow | Not described | MCP approval (docs) | Page claims runtime blocking | Yes: core | EU AI Act, NIST AI RMF | Lifecycle reviews | None on pages read |
| Behavox | No | No | No | No | Alignment claims | Archive and controls | Surveillance for banks |
| Perfios, PrivaTrust | Yes | No | PrivaTrust remediation hub | No | DPDP; PrivaTrust adds GDPR, CCPA | Consent records, processing records | India BFSI |
Based on the pages and sources named in each entry. “Not described” means not found on the pages we reviewed, not that the capability is absent. Many cells are vendor claims.
How do you choose an AI data privacy compliance platform for a bank?
Step 1: Map where customer data meets AIList the agents, copilots, vendors and employee tools that touch customer data. See AI agent inventory for banks.
Step 2: Classify what is sensitiveDecide which data classes matter, such as account numbers, card data and identity numbers, and where they live.
Step 3: Choose where limits are enforcedDecide whether limits sit at the endpoint, the gateway, the agent platform or the data store, and check traffic cannot bypass them.
Step 4: Decide block, redact or coachPick the action for each risk, since vendors differ on which actions each channel supports.
Step 5: Collect the vendor evidenceAsk for reports, scope, dates and expiry, and attach them to a third-party control. See SR 26-2 and the banking AI governance gap.
Step 6: Keep the proof togetherHold obligation, policy, control, test and evidence in one signed record, ready for a supervisor’s request.
| Question to ask a vendor | Why it matters |
|---|---|
| Which actions are real time, and which are scanned later? | Detection after the fact does not stop a leak. |
| Which channels support blocking, and which only alert? | Capabilities often differ by integration. |
| Where does the data and the metadata go? | A privacy tool can itself process sensitive data. |
| Which certifications cover the product, and when do they expire? | Claims without dates are hard to rely on. |
| Can the same person set a policy and approve it? | Separation of duties is a basic control. |
| How do I export logs as evidence? | The record is only useful if an examiner can read it. |
If your gap is the supervisor record, start with Madison. For related comparisons see our guides to regulatory change management software and AI agent observability, and the AI governance glossary.
See where your data controls and obligations connect
Bring your policy library and your AI vendor list to a Madison working session. You leave with a coverage map and a list of gaps.
Frequently asked questions
What are the best platforms for AI data privacy compliance in banks?
It depends on the job. In this comparison, BigID finds and classifies data, Nightfall controls data moving into AI tools, Mitratech Alyne, IBM watsonx.governance and ServiceNow govern AI, Behavox surveils communications, Perfios and PrivaTrust serve India’s DPDP Act, Opencontroller by Lyzr governs agent calls, and Madison holds the rules-to-evidence record an examiner reads. Most banks combine two or three.
What is AI data privacy compliance?
It means customer and employee data that enters, moves through or comes out of AI systems is handled as the bank’s privacy and security obligations require, and the bank can show it. That covers prompts, agent access to records, vendor processing and the evidence trail.
How do I stop employees pasting customer data into ChatGPT or other AI tools?
Use a data movement control that inspects prompts, files and agent calls and can block, redact or coach. Nightfall describes this across AI tools, MCP servers, SaaS and email, and BigID describes masking and access control in AI conversations. Also set a policy and train staff, and keep the record of what the control does.
What is the difference between data security platforms and AI governance platforms?
Data security platforms find, classify and control sensitive data. AI governance platforms inventory models and agents, assess their risk and manage approvals. Banks usually need both, plus a record linking them to the obligations. Madison is that record and does not scan data.
What is DSPM?
DSPM stands for data security posture management: discovering and classifying sensitive data across cloud and SaaS and showing who can reach it. BigID describes discovery and classification of this kind. DSPM finds where data is; it does not by itself stop it entering an AI tool.
Which US rules apply to AI and customer data in banks?
Vendors in this guide name GLBA, PCI DSS, SOX and NYDFS requirements, and supervisors have raised model risk guidance such as SR 11-7 and SR 26-2. Which apply depends on your charter and states, so confirm with counsel. This is not legal advice.
What is MCP security and why does it matter for data privacy?
MCP, the Model Context Protocol, lets agents call tools and read data sources. A tool call can carry sensitive data out or pull it in, so controls approve MCP servers, inspect calls and log them. Nightfall, ServiceNow and Opencontroller all describe MCP-related controls.
What is shadow AI?
Shadow AI is AI that processes, sends or stores company data outside approved governance, such as personal chat accounts, unregistered agents and unapproved MCP connections. Discovery tools build an inventory so it can be governed. Nightfall, IBM, ServiceNow and Opencontroller describe shadow AI or discovery features.
Do US banks need a DPDP compliance suite?
Only if they have operations or customers covered by India’s Digital Personal Data Protection Act. Perfios and PrivaTrust target that need. A US-only bank would usually focus on US requirements and, where relevant, GDPR.
Does Madison scan data or redact prompts?
No. Madison does not discover or classify data, inspect prompts, redact, block, manage consent or handle data subject requests. It holds vendors, models and agents as governed objects and connects the controls around them to policies, obligations and rules, with a named person signing each decision. Confirm with Lyzr how tool reports attach as evidence.
How does Opencontroller fit with data privacy tools?
Opencontroller by Lyzr is the agent control plane. It registers agents, enforces egress policy, authorizes each tool call, brokers credentials, requires separated approvals and keeps a signed audit trail. Its reference does not describe data classification or redaction, so it pairs with a data tool.
Is Behavox a data privacy tool?
No. Behavox describes communications surveillance, archiving and conduct controls, and says it holds ISO/IEC 42001 validated by Prescient Security. It is relevant because it handles sensitive communications, but its pages describe no consent, data discovery or subject request features.
Book A Demo: Click Here
Join our Slack: Click Here
Link to our GitHub: Click Here
Got a use case in mind?
8 weeks from use case to agents running in production.
Platform, people and FDEs, all in. Bring your environment. We'll co-build and stay until it's live.
Talk to UsFree resource
101 AI Agents Use Cases
100+ production-ready AI agent use cases across Marketing, Sales, HR, Banking, Insurance, Operations and a lot more
Download now